



 0 Comment
 Customer Reviews

The policy's been drafted. Legal signed off weeks ago. Somewhere in a shared drive, there's a compliance checklist nobody's touched since the initial audit.
That's how most CCPA readiness looks from the inside. Not chaos—just quiet neglect. The kind where everyone assumes someone else is handling the consumer data rights piece. Until a vendor asks. Or a regulator does.
Data privacy laws don't announce themselves before causing problems. The California Consumer Privacy Act gave businesses time to prepare. That time passed. What remains is the ongoing work of explaining—to boards, to clients, to internal teams—exactly where your data collection practices stand, what consumer opt-out options you've built, and why your privacy policy says what it says.
That's the part nobody trains for. The documentation is one thing. The presentation of that documentation is another. And there's a specific kind of discomfort that happens when a compliance officer has to stand in front of a leadership team and map out third-party data sharing exposure. Or when a legal team has to walk a client through GDPR vs CCPA differences without making it sound like they're guessing.
The frameworks exist. The regulations are clear enough—or at least documented enough. What's hard is turning that information into something a room full of non-lawyers can follow and act on.
So people made templates. Not because personal data protection is poorly understood, but because explaining it well requires structure. And structure, when you're dealing with sensitive personal information thresholds and data subject rights and opt-out obligations, is genuinely hard to build from scratch every time.
SlideTeam's pre-designed CCPA data templates handle exactly this—ready-made slides for the presentations that compliance, legal, and IT teams have to give repeatedly. Whether it's a board update on data privacy compliance status or a client-facing breakdown of what your privacy policy requires, these frameworks do the structural work.
Here's what's available across the collection.
Template 1: SDLC and Data Protection Regulations GDPR and CCPA PPT
Merges software development lifecycle discipline with data protection regulations for maximum clarity. The structured layout bridges GDPR and CCPA compliance frameworks in a single cohesive flow. Stakeholders instantly grasp where data privacy obligations intersect with your development process. Visual hierarchy keeps complex regulatory layers readable and actionable for every audience. Deliver compelling boardroom presentations on SDLC governance and data privacy compliance without losing critical detail. Transform your compliance presentations with confident, polished structure today. Download this dynamic template now and command every regulatory conversation with precision.
[product_image id=1424563]
Template 2: Navigating GDPR and CCPA Data Privacy Regulations PPT Presentation
Compliance conversations between legal, IT, and leadership rarely go smoothly without a clear visual anchor. This PPT template is built for compliance leads and privacy counsel walking teams through GDPR and CCPA data privacy regulations side by side. For context, it works well in cross-functional briefings where one team understands EU rules but not California Consumer Privacy Act obligations. The slide gives both frameworks equal, structured treatment. The template is 100% editable and customizable.
[product_image id=1415998]
Template 3: Navigating the Complexities of GDPR and CCPA Compliance PPT Summary
Captures the full scope of GDPR and CCPA compliance complexity without overwhelming your audience. Every slide translates dense regulatory language into structured, scannable frameworks your stakeholders can act on. The design balances legal rigour with visual accessibility for mixed technical and executive audiences. Color-coded sections drive instant clarity across data subject rights, consent obligations, and enforcement differences. Build authoritative compliance presentations that earn trust and demonstrate regulatory depth. Transform your privacy policy requirement briefings with this structured summary today. Download now and make complex data privacy regulations impossible to misread.
[product_image id=1454828]
Template 4: Navigating GDPR and CCPA Practical Compliance Strategies PPT
Practical compliance work rarely looks like theory—it looks like gap assessments, consent audits, and vendor reviews. This PPT preset is built for practitioners who need to present GDPR and CCPA compliance strategies to leadership without getting lost in legal text. It works especially well when walking a cross-functional team through opt-out rights implementation or data privacy framework alignment steps. The structure keeps every compliance action tied to a clear business obligation. The template is 100% editable and customizable.
[product_image id=1506507]
Template 5: Global Perspectives on Surveillance Capitalism GDPR vs CCPA Analysis
Surveillance capitalism is a real board-level conversation now—especially after GDPR vs CCPA comparisons entered mainstream regulatory discourse. This deck is built for policy analysts, legal teams, and consultants who need to present global data privacy regulations side by side with analytical depth. Use it to walk leadership through how different jurisdictions treat consumer data rights and what that means for cross-border operations. The structure handles both frameworks without flattening the nuance. The template is 100% editable and customizable.
[product_image id=1423946]
Template 6: Data Integration Unifying Silos for Smarter Decision Making PPT Guidelines
Fragmented data environments make compliance harder—and this deck addresses that directly. This PowerPoint slide is built for data architects and IT leads presenting data integration approaches to business stakeholders. It works well when showing how unified data infrastructure supports smarter decision-making and cleaner data collection practices across the organisation. The visual flow makes technical consolidation logic accessible to non-technical executives quickly. The template is 100% editable and customizable.
[product_image id=1847333]
Template 7: Data Inventory Management for GDPR and CCPA PPT
Drives complete visibility into your data inventory across GDPR and CCPA compliance requirements. Structured layouts map every data category, asset owner, and retention policy in one clean view. Stakeholders immediately see where third-party data sharing exposure exists within your system. The logical flow supports data protection officers conducting audits or presenting findings to executives. Build data inventory reviews that demonstrate accountability and regulatory readiness. Transform your compliance reporting presentations today. Download this authoritative template now and make data governance impossible to overlook.
[product_image id=1847334]
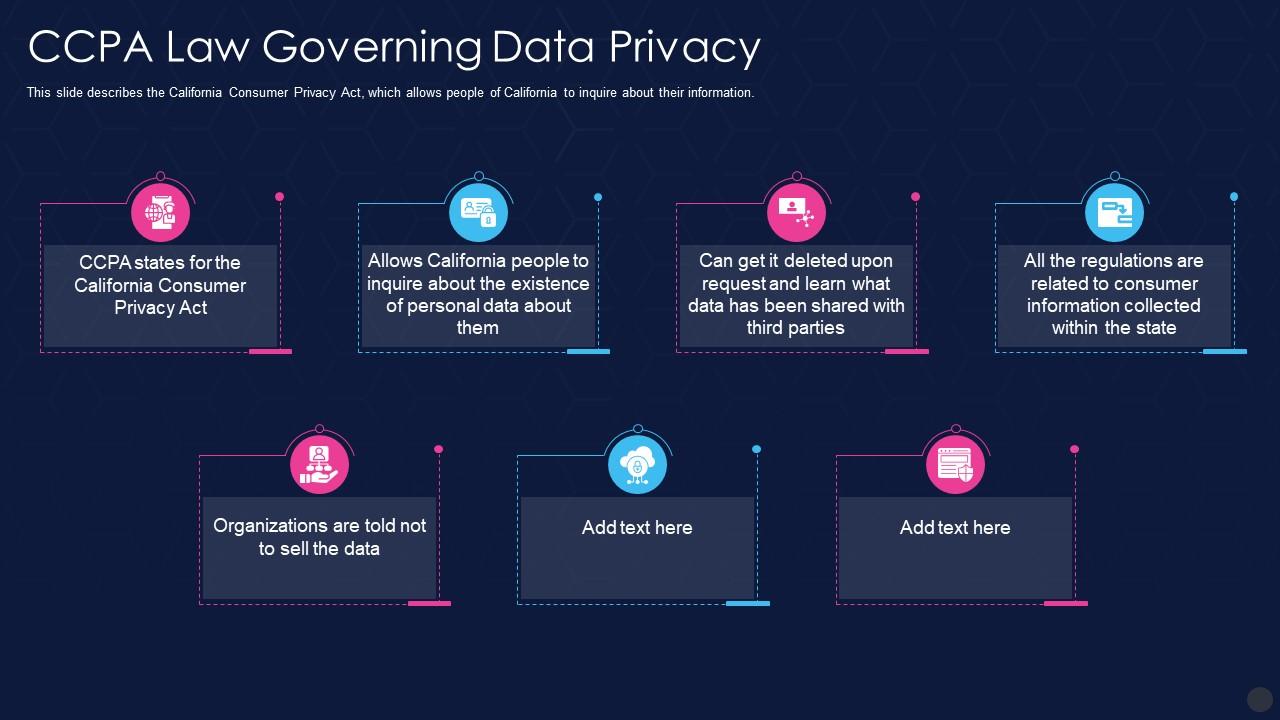
Template 8: Data Privacy IT CCPA Law Governing Data Privacy
Translates the California Consumer Privacy Act into a clear, presenter-ready visual framework. The seven-stage structure walks audiences through consumer inquiry rights, data disclosure obligations, and regulatory scope. Stakeholders gain an immediate working understanding of what CCPA requires from businesses. Visual consistency across all stages keeps the regulation accessible for both legal and non-legal audiences. Build foundational California Consumer Privacy presentations that educate and drive action confidently. Transform your data privacy law briefings today. Download this template now and make CCPA compliance your clearest conversation.
Download this PowerPoint Template
Template 9: CCPA Law Governing Data Privacy PPT Slides Infographic Template
Understanding the California Consumer Privacy Act starts with knowing exactly what personal data a business holds. This PPT preset breaks that down across five structured stages—covering consumer information rights, personal data existence, and disclosure obligations clearly. Privacy officers and compliance teams use it when preparing internal briefings or training sessions on consumer privacy rights. It turns dense regulation into a sequence any stakeholder can follow and retain. The template is 100% editable and customizable.

Download this PowerPoint Template
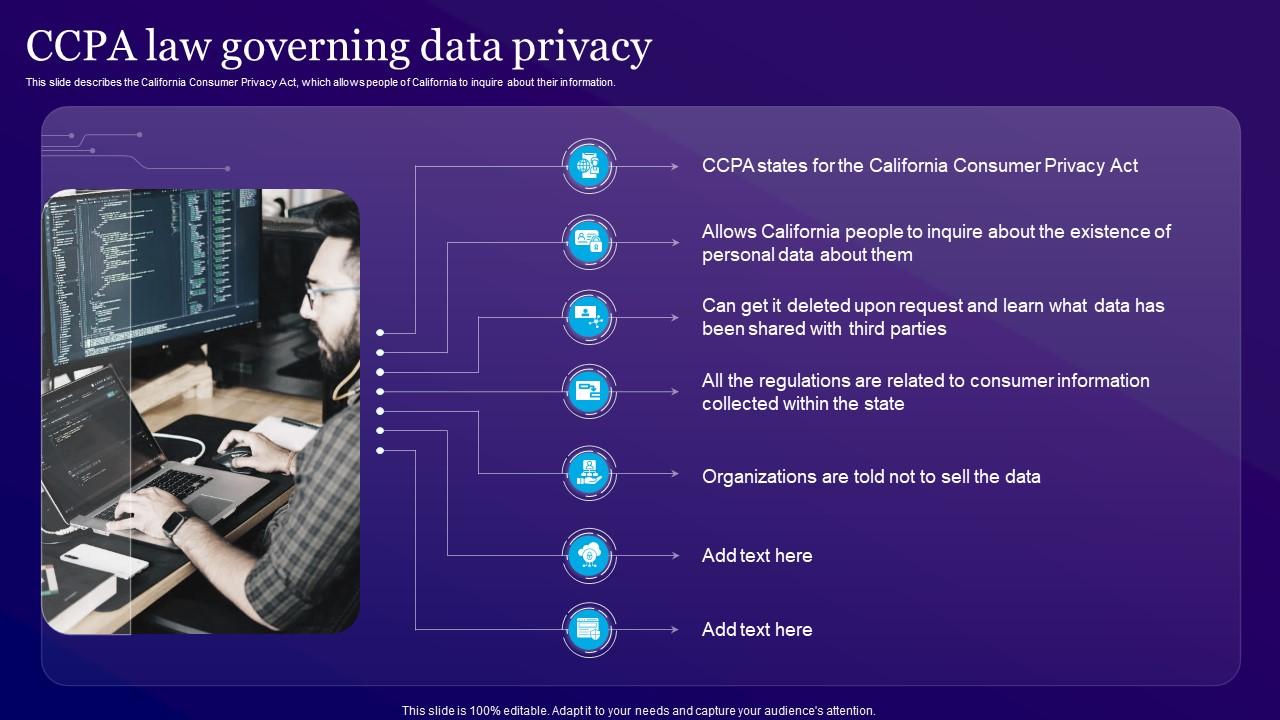
Template 10: CCPA Law Governing Data Privacy Information Privacy PPT PowerPoint Presentation
Most teams know CCPA applies to them—few can explain its seven key provisions clearly to a mixed audience. This slide is built for legal, HR, or compliance leads who need to present California Consumer Privacy Act obligations, covering personal data scope and consumer information rights, without overwhelming the room. It fits naturally into onboarding sessions, vendor briefings, or quarterly privacy reviews. The visual structure keeps every stage grounded and easy to follow. The template is 100% editable and customizable.
Download this PowerPoint Template
Master CCPA Data Compliance Presentations with SlideTeam
SlideTeam's PowerPoint templates are the best in the industry for CCPA data compliance presentations. These content-ready slides give compliance teams, legal counsel, and IT leaders the structure they need to communicate consumer data rights, opt-out obligations, and data privacy regulations clearly. Use these ready-made PowerPoint slides to turn complex regulatory requirements into boardroom-ready presentations. Deploy these templates to demonstrate accountability, build stakeholder confidence, and drive compliant business practices faster.
FAQs on CCPA Data
How does CCPA define "personal information" differently from GDPR, and what are the implications for businesses operating in both jurisdictions?
CCPA casts a wider net. It covers any information that identifies or is reasonably linked to a consumer or household—including inferred data. GDPR focuses on identified or identifiable natural persons and excludes household-level data. For businesses in both jurisdictions, this means your CCPA data inventory will likely be broader. Build separate compliance maps for each regulation rather than assuming one policy covers both.
What specific data categories does CCPA require businesses to disclose in their privacy policies, and how should presentation templates visually organize this information?
CCPA requires disclosure of data categories collected, the purpose for collection, categories of third parties receiving data, and consumer rights including opt-out and deletion. Visually, group these into four sections: what you collect, why, who gets it, and what consumers can do. A table or colour-coded matrix works well. Keep each section scannable—privacy policies are read under pressure, not leisure.
How can small businesses determine whether they meet the CCPA's threshold requirements for compliance?
CCPA applies if your business meets any one of three thresholds: annual gross revenue above $25 million, buying or selling personal data of 100,000 or more consumers or households annually, or deriving 50% or more of revenue from selling consumer data. Check each criterion separately. Most small businesses fall outside all three—but verify annually, as revenue and data volumes change.
What are the financial penalties for non-compliance with CCPA, and how do they differ between intentional and unintentional violations?
Unintentional violations carry civil penalties up to $2,500 per incident. Intentional violations jump to $7,500 per incident. The California Attorney General enforces these. Separately, consumers can sue for data breaches involving unencrypted personal information—statutory damages range from $100 to $750 per consumer per incident. Intentional violations compound fast at scale, so documented compliance processes matter significantly.
How should businesses structure their "Do Not Sell My Personal Information" opt-out process to meet CCPA requirements?
Place a clear "Do Not Sell My Personal Information" link on your homepage and any page where personal data is collected. The opt-out must require no account creation and must be honoured within 15 days. Document the request, update downstream vendor instructions, and keep records. Review the process annually—CCPA requires it to remain functional and accessible to all California consumers.
What role do data brokers play under CCPA, and how does the regulation affect their business models?
Data brokers collect and sell consumer information as their core business. Under CCPA, they must register with the California Attorney General annually and honour opt-out requests. The regulation directly constrains their resale model by giving consumers the right to stop data sales. Brokers must also disclose data categories sold and maintain clear processes for deletion requests.
How has the California Privacy Rights Act (CPRA) expanded upon the original CCPA framework?
CPRA, effective January 2023, added a new category—sensitive personal information—with stricter handling rules. It created the California Privacy Protection Agency to enforce the law. Consumers gained the right to correct inaccurate data. Data minimisation obligations were added, requiring businesses to collect only what is necessary. CPRA also extended opt-out rights to cover data sharing, not just data selling.
What are the key differences between a data controller and a data processor under CCPA, and why does this distinction matter for compliance?
CCPA does not use the controller/processor distinction the way GDPR does. It focuses on "businesses" and "service providers." A service provider processes data only on behalf of the business, under contract, and cannot use it for independent purposes. The distinction matters because service providers receive limited data-sharing restrictions. Misclassifying a vendor as a service provider when they act independently creates compliance exposure.