



 0 Comment
 Customer Reviews

The report's already filed. The breach happened three weeks ago.
Someone clicked a link. Probably looked legitimate—a spoofed login page, a credential harvester dressed up as an IT help desk ticket. And now there's a forensics team, a legal review, and a very uncomfortable board meeting scheduled for Thursday.
That's not a hypothetical. It's the pattern. Over and over, in companies that had policies, had IT teams, had passwords that met the minimum requirements. The problem isn't that nobody cared. The problem is that caring isn't the same as communicating clearly.
Because somewhere between the security team's findings and the executive presentation, something gets lost. The technical people know exactly what went wrong—misconfigured access controls, no endpoint monitoring, phishing awareness training that expired in 2021. But the people who need to act on it? They sat through a slide deck that was either too dense or too vague. They nodded. They approved nothing.
That gap—between knowing the problem and making other people understand it—is where most computer security efforts stall. It's not a knowledge gap. It's a presentation gap. And it shows up in incident response briefings, vulnerability assessment reviews, board-level risk reports, employee security training, you name it.
The templates exist because this problem is universal. Every security professional eventually needs to explain something complicated to someone who isn't technical. Every IT team eventually has to justify a budget, a policy change, or an emergency response to people who just want to know: are we safe, and what does it cost?
SlideTeam's computer security templates were built for exactly this situation—pre-designed frameworks that handle the structure so you can focus on the message. Content-ready slides covering everything from cyber threat landscapes to disaster recovery planning to zero trust architecture.
Here's what's in the collection.
Template 1: Computer Security PowerPoint Presentation Slides
Good computer security work rarely fails in the technical layer — it fails when decision-makers can't read the briefing. This PPT covers the core computer security concepts practitioners need to present clearly. A security analyst or IT lead reaches for this deck when walking stakeholders through cybercrime risks and protective measures. The 17 slides are structured to carry a complete narrative, from threat context to defensive posture. The template is 100% editable and customizable.
[product_image id=136080]
Template 2: Computer System Security PowerPoint Presentation Slides
Large security programs need structured decks that can hold 82 slides without losing coherence. This PPT preset is built for that — comprehensive enough for a full computer system security presentation, from policy frameworks to technical controls. Security leads and CISOs use it to walk cross-functional teams through IT security programs. Every concept gets its own slide without the deck feeling padded. The template is 100% editable and customizable.
[product_image id=454276]
Template 3: Computer System Security Cyber Threat Landscape in Computer Security
Understanding who is attacking you matters as much as knowing how they do it. This PowerPoint slide maps the cyber threat landscape by actor type — organized criminals, competitors, malicious insiders — and ties each to real business impact. Risk managers and security directors use this PPT in board-level cyber risk management conversations. It makes the threat feel concrete, not abstract. The template is 100% editable and customizable.
[product_image id=463307]
Template 4: Computer Security Presentation PPT Outline
Security presentations fail when the structure is unclear before a word is spoken. This slide deck gives practitioners a ready outline for a complete computer security presentation. It works for internal security briefings and external client-facing security reviews alike. The framework holds the narrative so the presenter can focus on content, not slide order. The template is 100% editable and customizable.
[product_image id=1470038]
Template 5: Computer Security Significance Organization Information Protection Verification System
Organizations often underestimate how much computer security ties back to identity and access verification. This PPT preset covers information protection and verification systems across 12 focused slides. IT managers and compliance leads use it to present security significance to leadership teams. The deck moves logically from organization-level risk to specific protective controls. The template is 100% editable and customizable.
[product_image id=270427]
Template 6: Computer System Security PPT Presentation
Boardroom security pitches and client-facing briefings have different audiences but one shared need — clarity. This PowerPoint slide is designed for computer system security presentations that need to land across technical and non-technical rooms. Security consultants and IT managers use it for pitches, audits, and internal reviews. The visual design carries credibility without overwhelming the content. The template is 100% editable and customizable.
[product_image id=1585530]
Template 7: Computer System Security Types of Disaster Recovery Plan
Disaster recovery planning for computer systems covers four distinct categories, and mixing them up during a presentation costs credibility. This template clarifies each type — data center, cloud-based, virtualization, and Disaster Recovery as a Service — with purpose-built slides for each stage. It drives clarity on cloud security continuity planning for IT leaders presenting recovery options. Download this template now and deliver disaster recovery plans that earn stakeholder confidence.
[product_image id=463293]
Template 8: Computer System Security of Employees Devices
Endpoint security isn't just about servers — employee devices are often the entry point for the most damaging breaches. This template addresses the security of employee hardware within a broader cybersecurity model, covering four key protection stages. It helps IT managers build a credible case for device-level security investment and policy. Use this slide to turn endpoint security discussions from abstract risk into concrete action. Download it now to strengthen your next security review.
[product_image id=463332]
Template 9: Protecting Data Best Practices in Computer Security PPT Designs
Data protection best practices don't sell themselves — they need clear framing to drive real behavior change. This deck is built for security teams presenting data breach prevention measures to both technical and non-technical audiences. Explore more computer security PPT templates and examples to find the right fit for your specific use case. The slides give practitioners a professional structure without starting from scratch. The template is 100% editable and customizable.
[product_image id=1485928]
Template 10: Computer System Security Post IT Notes PPT PowerPoint Presentation Slides
Sticky-note-style layouts make dense computer security concepts feel approachable rather than intimidating. This PPT design uses a Post-it note format to present information across three clear stages. Security trainers and team leads use it to break down complex topics for mixed-audience briefings. The visual format keeps attention where it belongs — on the message. Transform your computer security training sessions today. Download this dynamic template now and unlock audience engagement.
[product_image id=463325]
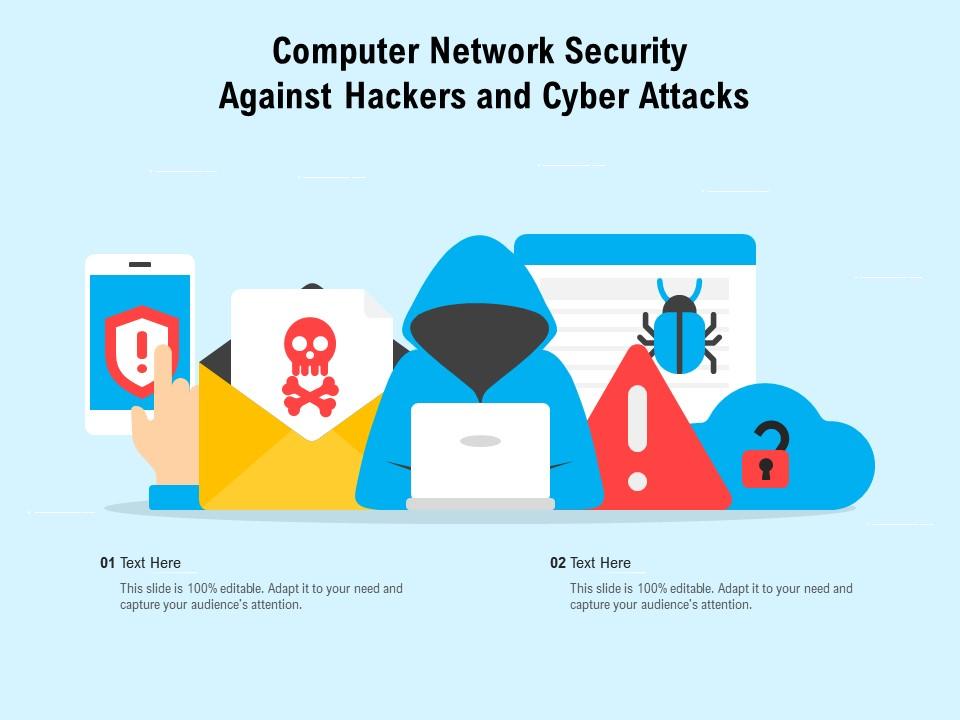
Template 11: Computer Network Security against Hackers and Cyber Attacks
Network security against hackers requires a presentation that matches the seriousness of the threat. This PowerPoint slide gives security professionals a clean, structured format for presenting network defenses and cyber attack prevention measures. IT leads and network security analysts use it for internal reviews and stakeholder updates. The deck makes technical security content accessible to non-technical decision-makers. The template is 100% editable and customizable.
Download this PowerPoint Template
Template 12: Essential Computer Security Measures for Data Protection PPT Guidelines
Essential computer security measures rarely get the visual treatment they deserve, which is why they don't land. This complete deck gives data protection presentations a polished, professional structure across every slide. Security managers and compliance officers use it to present security measures to leadership and audit committees. The design balances authority with clarity, keeping every key control visible. Transform your data protection presentations today. Download this dynamic template now and elevate your next security briefing.
[product_image id=1614635]
Template 13: Methods for Enhancing Computer Server Security
Server security is a multi-layered discipline — firewalls, antivirus, encryption, intrusion detection systems, and secure communications all interact. This template maps out seven methods for enhancing computer server security in a single, coherent visual flow. IT administrators and infrastructure leads use it to present server hardening plans to management. The seven-stage structure keeps even a complex security roadmap readable. Transform your server security presentations today. Download this template now and communicate your defense architecture with confidence.
[product_image id=1153099]
Template 14: Computer System Security Common Methods Used to Threaten Computer Security
Knowing the five common attack methods — malware, denial-of-service, man-in-the-middle, SQL injection, phishing — is standard. Presenting them in a way that drives real preventive action is harder. This PowerPoint slide maps each threat to its cause and prevention, giving security teams a practical briefing tool. IT security educators and risk leads use it for phishing attack prevention and malware protection awareness sessions. The template is 100% editable and customizable.
[product_image id=463302]
Template 15: Computer Protected with Information Security Software
Information security software decisions often get made without a clear visual framework, which slows approvals. This PPT preset walks through computer protection and information security software in a clean three-stage structure. IT procurement leads and security architects use it to justify software selection to budget-holders. The deck keeps the case for security investment direct and readable. The template is 100% editable and customizable.

Download this PowerPoint Template
Template 16: Computer System Security Types of Threats in Computer Security
Cybercrime, cyber terrorism, and cyberattacks are not the same thing — but they're often treated as if they are. This PowerPoint slide separates the three threat categories clearly, with purpose and impact mapped for each. Security educators and risk analysts use it to build shared vocabulary across teams before a deeper briefing. Getting the taxonomy right changes the quality of the conversation that follows. Transform your cybersecurity threat presentations today. Download this template now and drive sharper security awareness across your organization.
[product_image id=463337]
Template 17: Computer System Security What Are the Benefits of Computer Security
Security investment is easier to approve when the benefits are laid out clearly, not buried in technical language. This PPT covers five core benefits of deploying a computer security model — covering management, process, security devices, and potential threat reduction. CFOs and IT directors use it to make the business case for security spending in budget reviews. The five-stage layout keeps the argument crisp and stakeholder-friendly. The template is 100% editable and customizable.
[product_image id=463294]
Template 18: Computer Forensics Investigator Prevention Security Diagnosis Database Individual
Digital forensics and cybersecurity investigations need structured presentation frameworks as much as any other discipline. This complete 12-slide deck covers computer forensics investigation — prevention, diagnosis, and database management — in a cohesive visual package. Security analysts and IT investigators use it to present findings to legal teams, executives, and law enforcement liaisons. The thematic consistency across slides keeps complex forensic narratives readable. Transform your digital forensics presentations today. Download this template now and present investigation findings with clarity and authority.
[product_image id=380938]
Template 19: Computer System Security Elements of Computer Security Disaster Recovery Planning
Disaster recovery planning in cybersecurity requires clarity across four dimensions — business, technology, administration, and budget. This PowerPoint slide maps each element of a computer security disaster recovery plan in a structured four-stage format. IT continuity managers and security planners use it to build executive consensus around recovery investment. The layout makes resource allocation and financial decisions visible at a glance. Transform your disaster recovery presentations today. Download this template now and get recovery plans approved faster.
[product_image id=463288]
Template 20: Icon Depicting Computer Security from Cyber Threat
Visual icons carry meaning faster than paragraphs in a security briefing. This PPT preset provides a clean, purpose-built icon set depicting computer security protection against cyber threats. Security communicators and presentation designers use it to add visual clarity to any existing deck. The three-stage structure slots neatly into broader computer security presentations without disrupting the narrative flow. The template is 100% editable and customizable.

Download this PowerPoint Template
Elevate Every Computer Security Presentation with SlideTeam
SlideTeam's PowerPoint templates are the best in the industry for computer security presentations. These content-ready slides give security professionals the structure to communicate cyber threats, data breach prevention measures, and IT security policies with precision and authority. Use these ready-made frameworks to move faster from insight to action in every boardroom, audit, or team briefing. Deploy these PowerPoint slides and make every security conversation count.
FAQs on Computer Security
What are the most effective strategies for implementing a zero-trust security architecture in a hybrid cloud environment?
Zero trust in a hybrid cloud means no user or device is trusted by default — not even internal ones. Start with identity verification at every access point, enforce least-privilege access, and segment networks so lateral movement is blocked. Apply continuous monitoring across both on-premise and cloud workloads. Micro-segmentation and multi-factor authentication are the two controls that matter most at the implementation stage.
How do quantum computing advancements pose new threats to current encryption standards like RSA and AES?
Quantum computers can run Shor's algorithm, which factors large integers exponentially faster than classical machines. This breaks RSA directly, since RSA security depends on the difficulty of factoring. AES is weakened but not broken — its effective key length roughly halves, so AES-256 becomes roughly AES-128 in strength. The practical response is transitioning to post-quantum cryptography standards, which NIST began finalizing in 2024.
What distinguishes a polymorphic virus from a metamorphic virus in terms of evasion techniques?
A polymorphic virus mutates its code using encryption, but keeps the same underlying logic — only the decryption routine changes each time. A metamorphic virus rewrites its entire code body on each replication, with no consistent signature left to detect. Metamorphic viruses are harder to catch because there is no stable decryptor to find. Both evade signature-based detection, but metamorphic variants require behavioral analysis to identify.
How can organizations balance usability and security when enforcing multi-factor authentication across diverse user groups?
Start by segmenting users by risk level, not by convenience. High-privilege accounts — admins, finance, HR — get stricter multi-factor authentication without exception. General users can use push notifications or hardware tokens, which reduce friction significantly. The key is making the default secure option the easiest one. Usability problems come from poor implementation, not from multi-factor authentication itself.
What role does threat intelligence sharing play in strengthening collective cybersecurity defenses across industries?
Threat intelligence sharing lets organizations act on attacks that haven't hit them yet. When one company detects a new phishing campaign or malware signature, sharing that indicator of compromise gives others time to block it. Sector-specific groups — ISACs in financial services, healthcare, and energy — formalize this sharing. The practical value is speed: shared intelligence shrinks the window between a threat's appearance and an organization's defense.
How do attackers exploit misconfigured S3 buckets, and what automated tools can prevent such vulnerabilities?
Misconfigured S3 buckets are typically set to public read or public write, exposing data to anyone with the URL. Attackers use automated scanners to find these within hours of misconfiguration. AWS Config and cloud security posture management tools like Prisma Cloud or Orca Security detect and alert on public-access settings automatically. The fix is simple: enforce bucket-level block-public-access policies by default across every account.
What are the cybersecurity implications of adopting large language models within enterprise software ecosystems?
Large language models inside enterprise software introduce three concrete risks: data leakage through prompt inputs, prompt injection attacks, and over-privileged AI agents acting on unverified instructions. Sensitive data entered into LLM prompts may be used in training or exposed to other users. Organizations should treat LLM integrations like any third-party API — audit data flows, restrict what the model can access, and log every interaction for review.
How does a supply chain attack differ from a traditional malware attack in terms of detection and remediation?
A traditional malware attack enters through a known entry point — a phishing email, a vulnerable port. A supply chain attack hides inside trusted software updates or vendor code, so it arrives already authenticated. Detection is harder because the malicious code looks like legitimate activity from a known source. Remediation requires auditing every third-party dependency, not just the infected system — which makes the response significantly broader and slower.