



 0 Comment
 Customer Reviews

The policy document's been sitting in a shared drive for six months. Nobody's touched it.
Not because the threats aren't real—they are, and everyone knows it. But because building a cybersecurity framework from scratch means making decisions nobody feels qualified to make alone. Which controls matter most? Which regulations apply? Which risks actually get funding?
That's the uncomfortable part. The gap between knowing your organization needs structure and actually having one. Most security teams can describe the problem clearly. Far fewer can build the architecture that addresses it without second-guessing every layer.
Here's what compounds it: the options are overwhelming. NIST. ISO 27001. CIS Controls. MITRE ATT&CK. Zero Trust. Each has its own logic, its own vocabulary, its own advocates who'll tell you it's the one you should be using. And then there's the regulatory layer—IT security compliance requirements that shift, stack, and sometimes contradict each other. One framework for data protection standards. Another for critical infrastructure protection. A third for cloud environments.
Meanwhile, leadership wants a presentation. Not a whitepaper—a presentation. Something that explains where the organization stands, what's being done about it, and why the current approach holds up under scrutiny. That's a different skill set entirely. Understanding a cybersecurity framework is one thing. Making it legible to a board room is another.
So the templates exist. Not because frameworks are simple—they're not. They exist because the translation problem is universal. Every security team eventually needs to move from internal documentation to external communication. From technical controls to stakeholder clarity.
SlideTeam's cybersecurity framework templates were built for exactly that gap. Pre-designed slides that handle the structure so you can focus on the substance. Content-ready layouts for NIST, ISO 27001, risk dashboards, threat intelligence models, zero-trust architecture—the frameworks your organization is probably already working with.
Here's what's available.
Template 1: Implementing Cybersecurity Management Framework PowerPoint Presentation Slides
Fifty-five visually striking slides anchor this cybersecurity management framework deck. Each layout delivers structured, presentation-ready content built for security leaders. Use this cybersecurity framework template collection to present your security program with authority. Transform your management presentations today. Download this dynamic deck now and elevate your framework communications.
[product_image id=258680]
Template 2: Cybersecurity Risk Management Framework Information Security Risk Management Dashboard
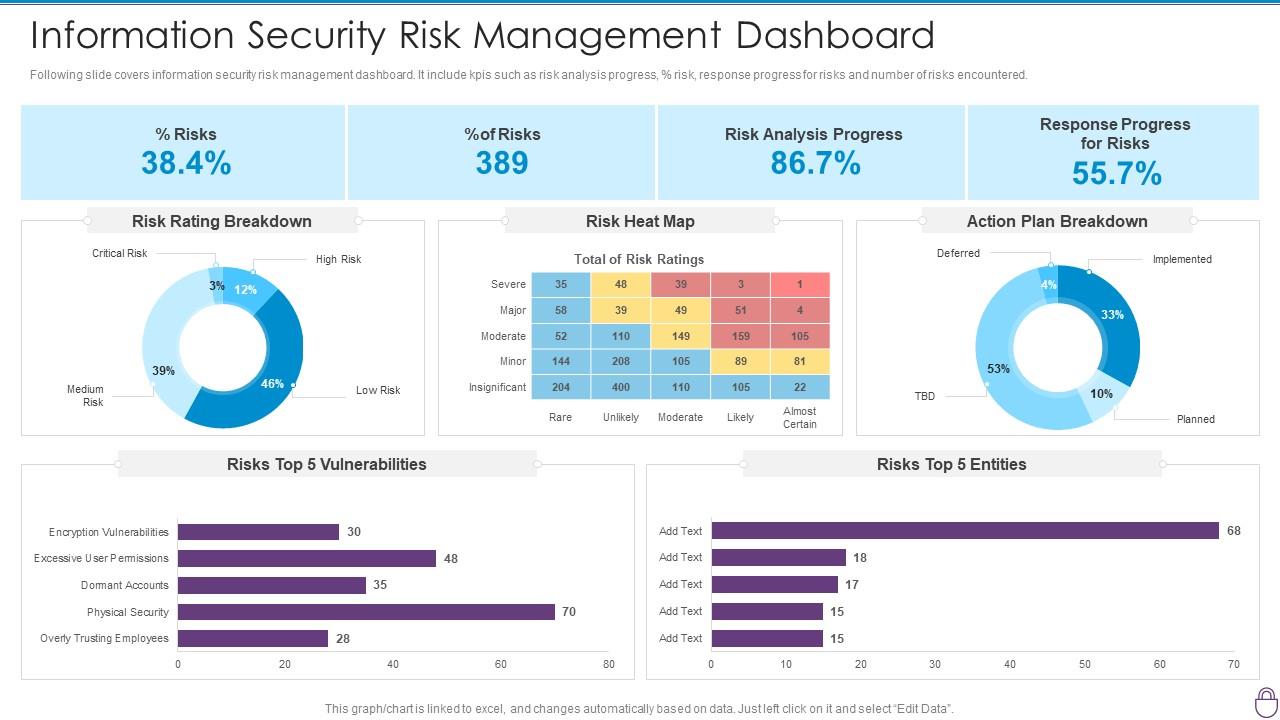
Instant visual clarity on security risk drives this information security risk management dashboard. KPIs including risk analysis progress, percent risk, and response progress are clearly displayed. The Risk Heat Map highlights your most urgent vulnerabilities at a glance. Action Plan Breakdown and Top 5 Vulnerabilities sections focus leadership attention immediately. Customizable layouts let you adapt every metric to your organization's context. Grab this cybersecurity risk management framework template for your next board-level review. Transform your risk reporting presentations today. Download this dashboard slide now and deliver sharper security governance.
Download this PowerPoint Template
Template 3: Cybersecurity Risk Management Framework PowerPoint Presentation Slides
Fifty-eight fully editable slides make this cybersecurity risk management deck remarkably versatile. Every slide adapts to your business context—fonts, colors, and graphics all modify effortlessly. Stylized layouts present complex risk concepts with visual confidence and clarity. The deck works as a complete delivery tool for your security team or stakeholders. No design expertise is needed to produce polished, persuasive results. Transform your cyber risk mitigation presentations today. Download this complete framework deck now and drive sharper security conversations.
[product_image id=538964]
Template 4: Cybersecurity Risk Assessment Program Nist Cybersecurity Framework with Subcategories
This slide maps the NIST Cybersecurity Framework with full subcategory detail for security teams. It identifies software solutions that satisfy multiple NIST compliance requirements simultaneously. Response Planning subcategories are clearly visualized for immediate operational use. Fully editable layouts let you personalize every element to your organization's needs. Use this NIST Framework template to present your compliance posture with precision. Transform your cybersecurity risk assessment presentations today. Download this template now and demonstrate your NIST readiness.

Download this PowerPoint Template
Template 5: Cybersecurity Integrated Framework to Manage Cyber Risk
Five structured stages—Identify, Protect, Detect, Respond, and Recover—anchor this integrated cyber risk framework. Each stage maps directly to real organizational security controls and practices. Steps include identifying data access users, securing networks, and updating antivirus systems. Disaster management planning is embedded within the framework's structured flow. Fully adaptable slide design ensures the layout fits any organization's threat environment. Transform your cyber threat assessment presentations today. Download this premium framework slide now and take control of your risk posture.

Download this PowerPoint Template
Template 6: Nist Cybersecurity Framework Overview Presentation PPT
Most IT security compliance conversations stall because the audience can't see the structure clearly. This PowerPoint slide gives security architects and CISOs a clean visual frame for presenting the NIST Framework across its core functions. It works well for cyber risk mitigation reviews or enterprise security architecture briefings where stakeholders need to grasp the full scope fast. For context, it also fits incident response framework discussions and regulatory compliance framework updates with leadership. The template is 100% editable and customizable.
[product_image id=1533585]
Template 7: Cybersecurity Framework Model Comparative Analysis
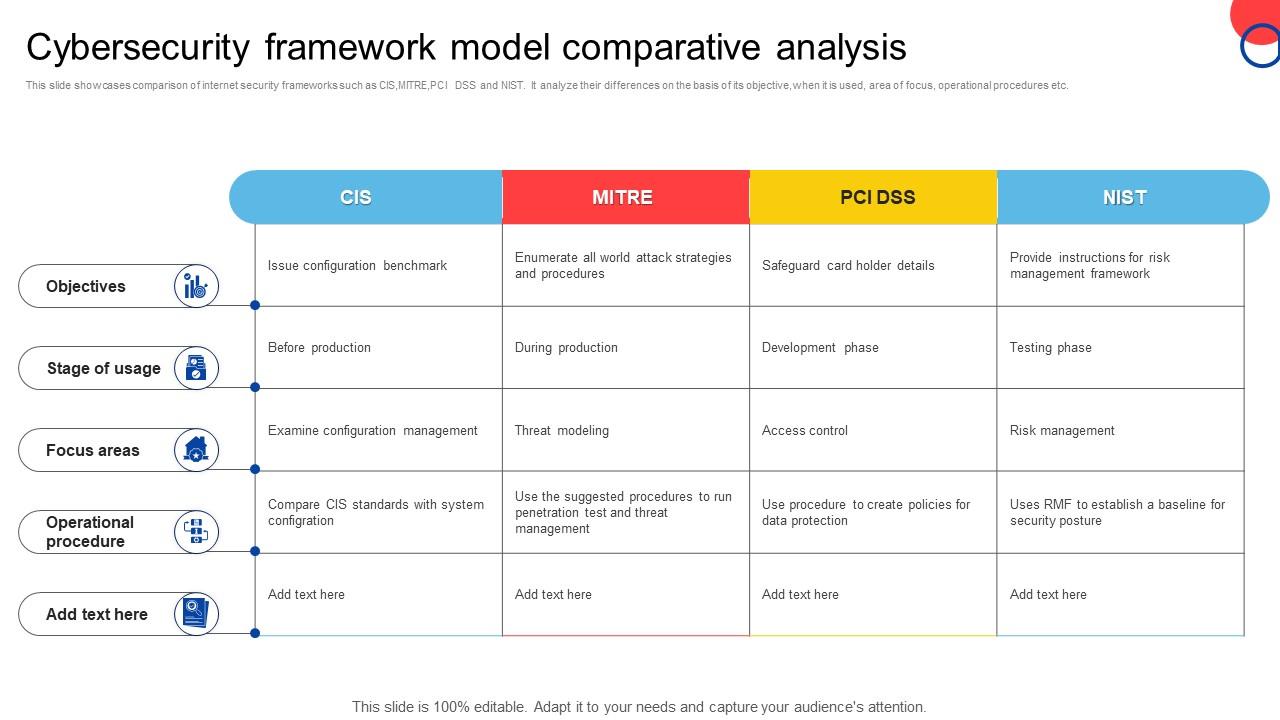
Side-by-side comparison of CIS, MITRE, PCI DSS, and NIST frameworks drives this analytical slide. Differences across objectives, usage stages, focus areas, and operational procedures are clearly mapped. Security leaders can use this visual to justify framework selection to executives instantly. The structured layout presents comparative data without overwhelming or cluttering the slide. Instantly editable in PowerPoint, this slide adapts to any organization's security governance narrative. Transform your security control framework comparison presentations today. Download this comparative analysis slide now and make your framework decision defensible.
Download this PowerPoint Template
Template 8: Strategy to Minimize Cyber Attacks Nist Cybersecurity Framework with Subcategories
Five NIST subcategory stages structure this cyber attack minimization framework slide clearly. Each subcategory maps to specific software that meets NIST compliance requirements in practice. The layout helps security teams communicate their attack-surface reduction strategy with precision. Visual stage design guides audiences through the framework logic without technical overload. Fully editable fields let you tailor subcategory details to your current security program. Transform your network security guidelines presentations today. Download this NIST subcategory template now and sharpen your cyber defense communication.

Download this PowerPoint Template
Template 9: Cybersecurity and Digital Business Risk Management Security Program Framework
Key components of an enterprise information security framework are laid out with clear structure. Context and leadership, evaluation and direction, prevention, and detection are all covered. Each component connects directly to real security program responsibilities and ownership areas. The slide supports security leaders presenting their program architecture to executive audiences. Fully editable design means every element adapts to your organization's specific framework model. Learn more through this resource on cybersecurity fundamentals and free templates. Transform your enterprise security architecture presentations today. Download this framework slide now and communicate your security posture with confidence.

Download this PowerPoint Template
Template 10: Action Plan to Combat Cyber Crimes Nist Cybersecurity Framework with Subcategories
Response Planning, Communications, Mitigation, and Security Continuous Monitoring are all structured here. This NIST subcategory slide maps your action plan for combating cyber crimes clearly. Detection Process steps are visually organized to guide teams through incident response priorities. Compliance requirements are identified alongside the software solutions that fulfill each one. Fully personalized layouts ensure the slide reflects your organization's current operational reality. Transform your incident response framework presentations today. Download this action plan template now and prepare your team for any cyber scenario.
[product_image id=937986]
Template 11: Security Plan to Prevent Cyber Nist Cybersecurity Framework with Subcategories
Anomalies and Events, Security Continuous Monitoring, and Protective Technology are all addressed here. This NIST subcategory framework slide structures your cyber prevention plan with precision. Compliance software requirements are mapped directly to each subcategory for actionable clarity. Security teams can use this slide to present their prevention posture to leadership quickly. Editable fields let you align every element with your current security program status. Transform your vulnerability management framework presentations today. Download this prevention-focused NIST slide now and fortify your security communications.
[product_image id=940772]
Template 12: Mitre Attandck Cybersecurity Threat Framework Tactics PPT Slides
MITRE ATT&CK tactics are visualized with striking design that commands attention in any boardroom. Creative layouts merge threat intelligence framework logic with clean, functional slide structure. Font, color, and content fields all customize freely to match your organization's voice. Compatible with Microsoft PowerPoint and Google Slides for effortless cross-platform presentation delivery. Download in JPG, JPEG, or PNG for easy distribution across security and leadership teams. This cybersecurity training module resource pairs well with this deck for workforce awareness. Transform your threat intelligence framework presentations today. Download this MITRE ATT&CK slide deck now and leave a lasting impression.
[product_image id=1226958]
Template 13: Implementing Nist Framework for Cybersecurity Success PPT
Implementing NIST framework principles becomes a visually compelling story with this full deck. Creative, versatile layouts keep audiences engaged from the first slide to the last. Brand-aligned color schemes and editable elements customize to your organization's identity quickly. Pre-designed structure saves preparation time without reducing your presentation's professional impact. Microsoft and Google Slides compatibility ensures smooth delivery in any presentation environment. Download in JPG, JPEG, or PNG for maximum sharing flexibility across teams. Transform your NIST cybersecurity framework success presentations today. Download this fully editable deck now and make your implementation story undeniable.
[product_image id=1583377]
Template 14: Cybersecurity Risk Assessment Program Framework for Cybersecurity Risk Assessment
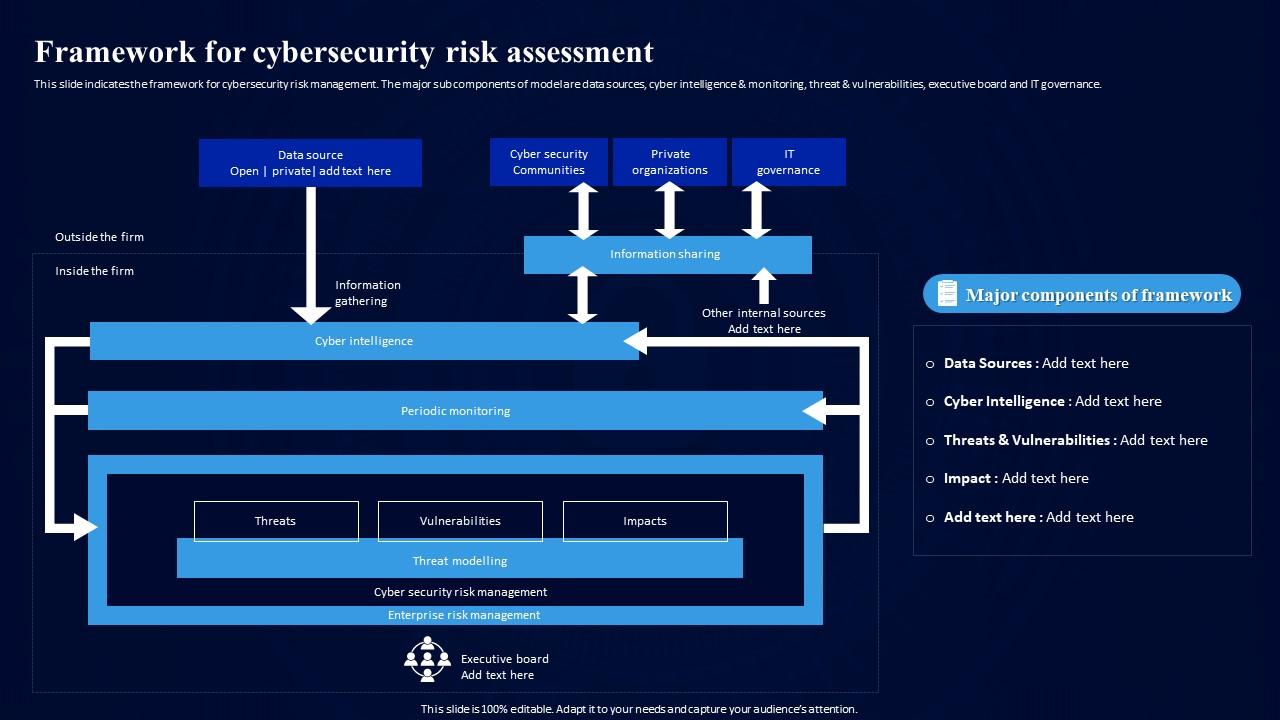
Data sources, cyber intelligence, threat and vulnerabilities, and IT governance anchor this risk assessment framework. Executive board visibility is built directly into the model's subcomponent structure. The slide communicates how cyber intelligence and monitoring feed into organizational decision-making. Security and IT governance leaders can present this model to justify investment and structure. Every element is fully editable, making personalization to your organization's context straightforward. Transform your cybersecurity risk assessment program presentations today. Download this framework slide now and make your risk model defensible to any audience.
Download this PowerPoint Template
Template 15: Effective Cybersecurity Program Management Framework
Early threat detection methodology is built into this cybersecurity program management framework. Strategic roadmap, data-driven innovation, and defined audience structure the program's four pillars clearly. Scalable Architecture and Integrated Systems are visualized for immediate executive comprehension. Cultural and experiential dimensions of security program management are represented alongside technology elements. Instantly customizable slides ensure this deck adapts to your organization's maturity and priorities. Transform your cybersecurity program management presentations today. Download this framework set now and make your security strategy clear to every stakeholder.
[product_image id=1148317]
Template 16: Understanding the Cybersecurity Framework PPT Outline
Most organizations adopting NIST Framework or ISO 27001 Framework standards struggle to explain the structure clearly to non-technical stakeholders. This PPT template gives IT security and governance teams a clean outline to walk through cybersecurity risk management without losing the room. A CISO or compliance lead can use it to map enterprise security architecture, cover data protection standards, and anchor an IT security compliance review. It keeps complex frameworks readable. The template is 100% editable and customizable.
[product_image id=1551747]
Template 17: Building a Robust Cybersecurity Framework PPT Example
Most organizations treat cybersecurity as a checklist, not a system — and that gap shows up during audits and incidents alike. This PPT template is built for IT security leads and CISOs who need to present an enterprise security architecture clearly and credibly. It works well for mapping out a NIST Framework alignment, walking stakeholders through an ISO 27001 Framework gap analysis, or anchoring a cyber risk mitigation roadmap. Solid structure for a Security Governance Framework conversation, without the noise. The template is 100% editable and customizable.
[product_image id=1516433]
Template 18: Introduction to the Cybersecurity Framework PPT Example
Most organisations know they need a cybersecurity framework — few can explain one clearly to a mixed room. This PPT template gives IT security and compliance leads a clean, structured way to introduce foundational concepts: what a Security Governance Framework covers, where NIST Framework controls sit, and how ISO 27001 Framework principles connect to everyday IT Security Compliance decisions. It suits onboarding sessions, audit prep briefings, or an Enterprise Security Architecture kickoff equally well. The template is 100% editable and customizable.
[product_image id=1555747]
Elevate Your Cybersecurity Framework Presentations with SlideTeam
SlideTeam's PowerPoint templates are the best in the industry for cybersecurity framework communication. These content-ready slides cover everything from NIST compliance and ISO 27001 alignment to risk dashboards and incident response planning—saving your team hours of design work. Ready-made layouts give you professional structure that builds credibility with executives, boards, and regulators alike. Grab these templates to transform your security governance narrative and drive the organizational buy-in your framework deserves.
FAQs on Cybersecurity Framework
What are the core components that differentiate a proactive cybersecurity framework from a reactive one?
A proactive framework acts before incidents happen; a reactive one responds after. The key differentiators are continuous monitoring, threat intelligence feeds, and pre-defined risk thresholds. Proactive frameworks embed regular security risk assessments into normal operations. Reactive frameworks typically activate only after a breach is detected or reported.
How does the NIST Cybersecurity Framework align with ISO 27001 standards, and where do they diverge?
Both NIST and ISO 27001 address risk management and security controls, but they differ in scope. NIST is a voluntary US government framework focused on critical infrastructure; ISO 27001 is a certifiable international standard. NIST uses five functions—Identify, Protect, Detect, Respond, Recover. ISO 27001 requires formal audits and documented evidence for certification.
Which cybersecurity framework is most suitable for small-to-medium enterprises with limited IT budgets?
The CIS Controls framework is the most practical starting point for small-to-medium enterprises. Its 18 prioritized controls are organized by implementation group, so limited-budget teams start with the highest-impact actions first. It requires no certification fees. Many tools that map to CIS Controls are open-source or low-cost.
How can organizations measure the effectiveness of their implemented cybersecurity framework over time?
Track KPIs such as mean time to detect, mean time to respond, and the number of unmitigated vulnerabilities over time. Run regular security risk assessments against your baseline. Conduct tabletop exercises annually to test your incident response plan. Third-party audits provide an unbiased measure of your framework's real-world effectiveness.
What role does threat intelligence play in strengthening the identify function of the NIST framework?
Threat intelligence feeds the Identify function by mapping known adversary tactics to your asset inventory. It tells you which threats are actively targeting your industry right now. Teams use this data to prioritize which vulnerabilities actually need urgent remediation. Without threat intelligence, the Identify function defaults to theoretical risk rather than real, current exposure.
How do zero-trust architecture principles integrate with existing cybersecurity frameworks?
Zero Trust operates on the principle of 'never trust, always verify'—this maps directly onto the Protect and Detect functions of most frameworks. Organizations integrate it by applying identity verification and least-privilege access controls across all existing security layers. It doesn't replace a framework; it tightens the controls already required. NIST SP 800-207 provides the formal integration guidance.
What are the most common gaps organizations face when transitioning from ad hoc security practices to a formal cybersecurity framework?
The most common gaps are missing asset inventories, undefined roles and responsibilities, and no formal incident response plan. Organizations often have tools but no documented processes connecting them. Policies exist on paper but haven't been tested against real scenarios. Closing these gaps requires mapping current controls to the chosen framework before adding anything new.
How does the CIS Controls framework prioritize security actions differently from COBIT?
CIS Controls prioritize actions by impact and implementation difficulty—start with the highest-risk, lowest-effort fixes first. COBIT prioritizes IT governance alignment with business goals and regulatory requirements. CIS is operational and technical; COBIT is managerial and process-oriented. Most mature organizations use CIS Controls for day-to-day security operations and COBIT for executive reporting and audit readiness.