

Endpoint-Sicherheits-Präsentationsfolien


Try Before you Buy Download Free Sample Product
 Impress Your
Audience
 100%
Editable
 Save Hours
of Time


Unsere professionell gestaltete Endpoint Security PowerPoint-Präsentation. Sie erklärt kurz die Übersicht über Endpoint-Sicherheit, ihre Komponenten, gängige Bedrohungen und Vorteile. Die Präsentation enthält auch die verschiedenen Elemente der Endpoint-Sicherheit. Darüber hinaus enthält diese Präsentation zu den Grundlagen der Endpoint-Sicherheit die Komponenten der Endpoint-Sicherheit, darunter Antiviren-Software, Firewall, Intrusion Detection und Präventionssystem, Verschlüsselung, Patch-Management usw. Darüber hinaus umfasst unsere Endpoint Security Deployment Template den Arbeitsprozess, die Schritte zur Implementierung und eine Marktanalyse der Endpoint-Sicherheit. Schließlich skizziert diese Endpoint Security Components PowerPoint-Präsentation bewährte Verfahren, eine Checkliste, ein Schulungsbudget, einen Zeitplan, einen Fahrplan und die Auswirkungen der Endpoint-Sicherheit. Laden Sie unsere zu 100 Prozent bearbeitbare und anpassbare Vorlage herunter, die auch mit Google Slides kompatibel ist.
People who downloaded this PowerPoint presentation also viewed the following :
Inhalt dieser Powerpoint-Präsentation
Folie 1: Die Folie führt in die Endpoint-Sicherheit ein. Nennen Sie Ihren Firmennamen und beginnen Sie.
Folie 2: Dies ist eine Agenda-Folie. Geben Sie hier Ihre Tagesordnungspunkte an.
Folie 3: Die Folie zeigt den Titelinhalt für die Präsentation.
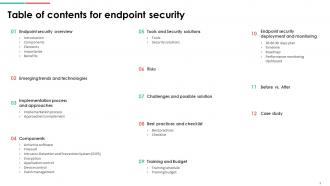
Folie 4: Die Folie führt das Inhaltsverzeichnis fort.
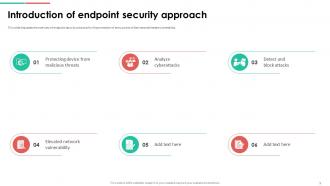
Folie 5: Diese Folie erläutert die Übersicht über Endpoint-Sicherheitslösungen zum Schutz der Eingangspunkte von Geräten und zur Erhöhung der Sicherheit.
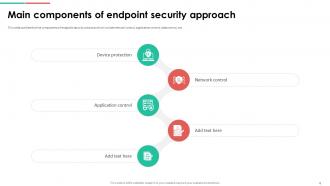
Folie 6: Diese Folie umreißt die fünf Komponenten von Endpoint-Sicherheitslösungen, zu denen Netzwerkkontrolle, Anwendungskontrolle, Datenkontrolle usw. gehören.
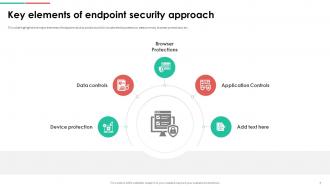
Folie 7: Diese Folie hebt die wichtigsten Elemente von Endpoint-Sicherheitslösungen hervor, zu denen Geräteschutz, Datenkontrollen, Browser-Schutz usw. gehören.
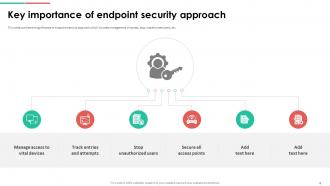
Folie 8: Diese Folie umreißt die Bedeutung des Endpoint-Sicherheitsansatzes, der das Zugriffsmanagement, das Stoppen unbefugter Benutzer usw. umfasst.
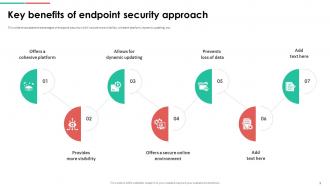
Folie 9: Diese Folie zeigt die Vorteile der Endpoint-Sicherheit, zu denen mehr Sichtbarkeit, eine kohärente Plattform, dynamische Aktualisierungen usw. gehören.
Folie 10: Die Folie zeigt einen weiteren Titelinhalt.
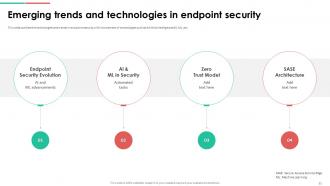
Folie 11: Diese Folie umreißt die Technologien und Trends in der Endpoint-Sicherheit mit Technologien wie Künstlicher Intelligenz (KI), ML usw.
Folie 12: Die Folie zeigt einen weiteren Titelinhalt, der noch besprochen wird.
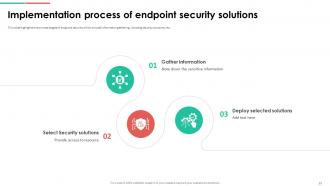
Folie 13: Diese Folie hebt die Prozessstufen der Endpoint-Sicherheit hervor, zu denen die Informationsbeschaffung, die Auswahl von Sicherheitslösungen usw. gehören.
Folie 14: Diese Folie zeigt die Techniken für die Implementierung einer effektiven Endpoint-Sicherheit, zu denen On-Premises-, Cloud- und Hybrid-Endpoint-Sicherheit gehören.
Folie 15: Die Folie zeigt einen weiteren Titelinhalt.
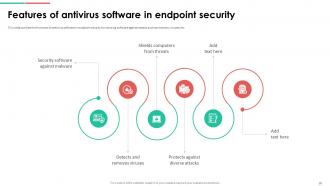
Folie 16: Diese Folie umreißt die Funktionen von Antivirensoftware in der Endpoint-Sicherheit zum Schutz von Software vor Angriffen wie Malware, Viren usw.
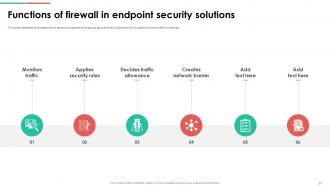
Folie 17: Diese Folie stellt die Ziele der zweiten Komponente der Endpoint-Sicherheit, der Firewall, dar, die zur Überwachung des Datenverkehrs von Geräten verwendet wird.
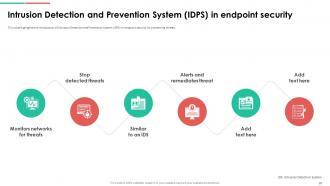
Folie 18: Diese Folie hebt die Einführung des Intrusion Detection and Prevention Systems (IDPS) in der Endpoint-Sicherheit zur Verhinderung von Bedrohungen hervor.
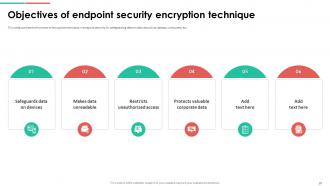
Folie 19: Diese Folie umreißt die Funktionen der Verschlüsselungstechnik in der Endpoint-Sicherheit zum Schutz von Daten auf Geräten wie Laptops, Computern usw.
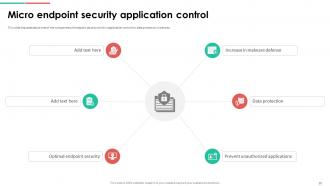
Folie 20: Diese Folie erläutert eine der Komponenten der Endpoint-Sicherheit, die Anwendungskontrolle zum Datenschutz auf Geräten.
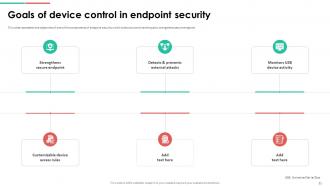
Folie 21: Diese Folie stellt die Ziele einer der Komponenten der Endpoint-Sicherheit, der Gerätekontrolltechnik, dar, um die Endpoint-Sicherheit zu stärken.
Folie 22: Diese Folie umreißt die Übersicht über die Patch-Management-Technik in der Endpoint-Sicherheit zum Scannen, Identifizieren, Herunterladen und Bereitstellen von Patches.
Folie 23: Die Folie zeigt einen weiteren Titelinhalt.
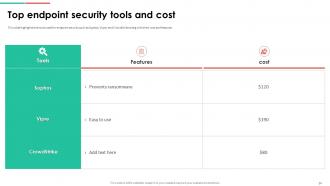
Folie 24: Diese Folie hebt die für die Endpoint-Sicherheit verwendeten Tools wie Sophos, Vipre und CrowdStrike sowie deren Kosten und Funktionen hervor.
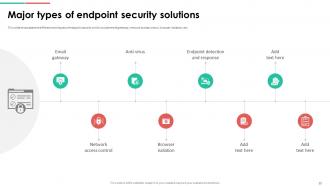
Folie 25: Diese Folie zeigt die verschiedenen Techniken der Endpoint-Sicherheit, zu denen E-Mail-Gateway, Netzwerkzugangskontrolle, Browser-Isolation usw. gehören.
Folie 26: Die Folie zeigt einen weiteren Titelinhalt.
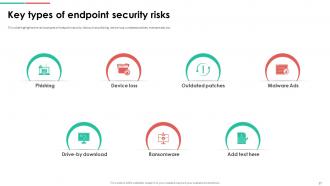
Folie 27: Diese Folie hebt die verschiedenen Arten von Endpoint-Sicherheitsrisiken wie Phishing, Geräteverlust, veraltete Patches, Malware-Anzeigen usw. hervor.
Folie 28: Die Folie zeigt auch einen Titelinhalt.
Folie 29: Diese Folie erläutert die Risiken und entsprechenden Lösungen der Endpoint-Sicherheit, zu denen menschliches Verhalten, unzusammenhängende Sicherheitslösungen usw. gehören.
Folie 30: Die Folie zeigt einen weiteren Titelinhalt.
Folie 31: Diese Folie erläutert die besten Ansätze für die Implementierung der Endpoint-Sicherheit, zu denen Anti-Phishing-Bereitstellung, Ransomware-Schutz usw. gehören.
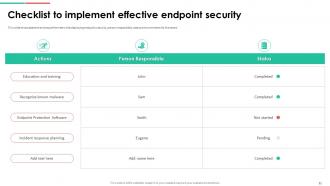
Folie 32: Diese Folie zeigt die bei der Implementierung der Endpoint-Sicherheit durchgeführten Aktionen, die verantwortliche Person, den Status und Kommentare dazu.
Folie 33: Die Folie zeigt einen weiteren Titelinhalt.
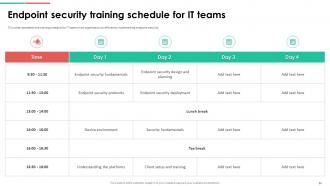
Folie 34: Diese Folie zeigt den Schulungsplan für IT-Teams in einem Unternehmen zur effizienten Implementierung der Endpoint-Sicherheit.
Folie 35: Diese Folie zeigt die Technologiekostenaufschlüsselung für verschiedene Komponenten wie Internet, Software, IT-Mitarbeiter usw.
Folie 36: Die Folie hebt einen weiteren Titelinhalt hervor.
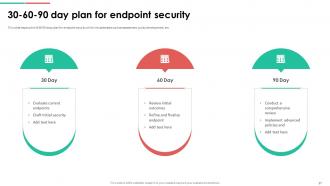
Folie 37: Diese Folie zeigt den 30-60-90-Tage-Plan für die Endpoint-Sicherheit mit Aufgaben wie Bewertung, Richtlinienerstellung usw.
Folie 38: Diese Folie umreißt die verschiedenen Schritte bei der Implementierung der Endpoint-Sicherheit, einschließlich der Planungsphase, der Lösungsauswahl usw.
Folie 39: Diese Folie zeigt die Schritte zur Implementierung der Endpoint-Sicherheit, zu denen die Erkennung bekannter Malware, die Reduzierung des Endbenutzerzugriffs, die Nutzung der Anwendungskontrolle usw. gehören.
Folie 40: Diese Folie zeigt das Leistungsverfolgungsdashboard für die Endpoint-Sicherheit zur Analyse und Überwachung der Sicherheit von Geräten wie Laptops.
Folie 41: Die Folie zeigt einen weiteren Titelinhalt.
Folie 42: Diese Folie zeigt eine Vergleichsanalyse der Situation vor und nach der Implementierung der Endpoint-Sicherheit in einem Unternehmen.
Folie 43: Die Folie zeigt einen weiteren Titelinhalt.
Folie 44: Diese Folie hebt die Übersicht über das Unternehmen, die aufgetretenen Probleme und die entsprechenden Lösungen in der Fallstudie hervor.
Folie 45: Diese Folie zeigt alle in der Präsentation enthaltenen Symbole.
Folie 46: Diese Folie trägt den Titel "Zusätzliche Folien für den Fortschritt".
Folie 47: Dies ist unsere Standort-Folie mit zugehörigen Symbolen und Text.
Folie 48: Diese Folie zeigt Post-It-Notizen. Notieren Sie hier Ihre wichtigen Notizen.
Folie 49: Dies ist eine Folie zur Ideengenerierung, um eine neue Idee zu nennen oder Informationen, Spezifikationen usw. hervorzuheben.
Folie 50: Diese Folie zeigt eine SWOT-Analyse mit Stärken, Schwächen, Chancen und Risiken.
Folie 51: Dies ist unsere Ziel-Folie. Geben Sie hier Ihre Ziele an.
Folie 52: Dies ist eine Zeitachse. Zeigen Sie hier Daten zu Zeitintervallen an.
Folie 53: Diese Folie enthält ein Puzzle mit zugehörigen Symbolen und Text.
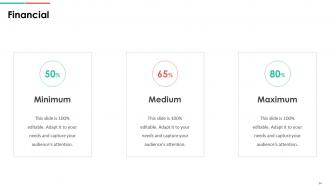
Folie 54: Dies ist eine Finanz-Folie. Zeigen Sie hier Ihre finanzrelevanten Inhalte an.
Folie 55: Dies ist eine Dankeschön-Folie mit Adresse, Telefonnummern und E-Mail-Adresse.
Endpunkt-Sicherheits-Präsentationsfolien mit allen 64 Folien
Verwenden Sie unsere Endpoint Security Powerpoint-Präsentationsfolien, um Ihre wertvolle Zeit effektiv zu sparen. Sie sind fertig erstellt, um in jede Präsentationsstruktur zu passen.

























FAQs for Endpoint Security
Look, you need four things for decent endpoint security: antivirus/anti-malware, EDR tools, patch management, and access controls. Most places screw up the EDR part - they stick with basic antivirus thinking it'll do the job. It won't. Also throw in regular vulnerability checks and backup everything because ransomware will wreck your day. Oh, and layer this stuff so when one thing fails, something else catches it. I'd start by checking what you've got now and fixing the worst gaps first. Trust me on the backup thing though - seen too many companies get absolutely destroyed by ransomware.
So basically endpoint security protects your actual devices - laptops, phones, whatever - while network security is more about guarding the gates and monitoring traffic between systems. Picture locking your car vs having guards at the parking garage entrance. Network security used to work fine when everyone sat in offices behind corporate firewalls. But now? Your devices are literally everywhere - Starbucks, home, that sketchy airport wifi. Each device needs its own armor since it can't count on network protection anymore. Honestly, I'd start by checking what endpoint stuff you've even got running right now.
Look, you're mainly dealing with malware - ransomware, trojans, the usual suspects. Phishing attacks hit your users constantly, and credential theft is huge right now. Insider threats are tricky since they can be accidents or actual malicious stuff. Unpatched systems? Attackers absolutely love those. USB threats sound ancient but they're still around, weirdly enough. APTs are the worst because they lurk for months undetected. Honestly, just layer everything - get some solid EDR tools, stay on top of patches, train your people, and lock down access properly. That'll handle most scenarios.
Honestly, I'd start by making a list of every single device that touches your network - phones, laptops, even those random IoT things you forgot about. Run vulnerability scans on everything to catch outdated software and missing patches. Yeah, it's boring but whatever. Check your current security stuff too - antivirus, encryption, access controls - and see what's missing. Your users are probably the biggest risk though... they'll click anything. Document it all in some kind of risk matrix, then tackle the scariest stuff first. Way easier than trying to fix everything at once.
So threat intelligence basically gives your endpoint tools a heads up about what hackers are doing right now. Your systems can spot new attack patterns and sketchy behavior before it actually hits you. It's kinda like having someone text you "hey, break-ins happening on Oak Street" so you know to lock up. The feeds update your detection rules automatically - honestly way better than trying to keep up manually because that's exhausting. Just make sure you're getting decent quality feeds though, otherwise you're basically guessing what the bad guys will try next.
Ugh, mobile devices have totally blown up our attack surface - it's honestly a nightmare. Now we're juggling personal phones, BYOD chaos, sketchy apps from random stores, plus people working from literally everywhere. Coffee shops, sketchy WiFi, you know the drill. These devices don't have the same solid security controls as corporate laptops either. Remember when we had an actual network perimeter? Those days are dead. Sarah's probably pulling up sensitive files on her cracked iPhone screen right now from some random Starbucks. You'll need proper mobile device management and zero-trust architecture to not lose your mind over this stuff.
Oof, cost is brutal - these solutions get pricey quick when you're talking hundreds of devices. Users will absolutely hate you for it too, constant whining about slow laptops and blocked apps. Managing updates across different systems is a nightmare. Oh, and good luck getting consistent coverage on mixed environments. Honestly though, don't go full company rollout right away. Test it with like 20-30 people first so you can fix whatever breaks before everyone's screaming at IT.
So instead of just catching known threats, AI and ML make your endpoint security predictive - it learns patterns to spot sketchy behavior in real-time. Pretty neat stuff. The system analyzes file behavior, network traffic, user activities, all that. Even flags things it's never seen before if they look suspicious. Over time the algorithms get better at learning what's normal in your environment, so you get fewer false alarms but catch more actual threats. Oh and definitely look for solutions with behavioral analysis rather than the old signature-based detection - way more effective.
Phishing simulations are your best bet - way more effective than boring presentations nobody remembers. Do short monthly sessions instead of those painful quarterly workshops. Cover the obvious stuff like sketchy emails, strong passwords, software updates. Real examples from your field work great too. Here's the thing though - you need people to feel safe reporting weird stuff without getting yelled at. I've watched companies get totally wrecked because someone was too scared to speak up about a suspicious link. Set up an easy reporting system and actually make it interactive. People learn better when they're doing something, not just sitting there zoning out.
So basically, endpoint security hooks up to cloud services through APIs and integrations - gives you one dashboard to monitor all your devices. Pretty handy since everyone's working from random places now. The cloud handles threat updates and policy stuff automatically, which is nice because who has time for that? Most solutions play well with AWS or Azure too. Main thing is you don't need those bulky on-site servers anymore. Just heads up though - if your internet goes down, you're kinda screwed since everything runs through the cloud. But honestly, that's most tech these days anyway.
Track your incident response times and malware detection rates first - those are your bread and butter. MTTD and MTTR will show you how fast you're catching stuff and fixing it. Endpoint compliance is huge too (basically how many devices follow your security rules). False positives are annoying as hell, so definitely monitor those. Nobody wants constant alerts about nothing. User training completion matters since people click on literally everything. Oh, and set up a monthly dashboard so you can actually see trends and show your boss you're not just burning money on security tools.
So zero-trust basically throws out the whole "trust but verify" thing (which honestly never made sense to me either). Instead of assuming devices inside your network are safe, you treat everything like it's already compromised. Every endpoint gets constantly checked - device health, user identity, app behavior - before it can access anything. Your endpoint security agents have to get way smarter too. They're not just hunting for threats anymore; they're making real-time decisions about whether each connection should even happen. It's like having a bouncer at every digital door instead of just the front entrance.
Remote work completely blows up your security setup. Suddenly people are logging in from their kitchen table WiFi, random coffee shops, wherever. Gone are the days when everyone's safely behind your corporate firewall. Personal laptops start creeping into work tasks too - honestly drives IT teams nuts trying to track everything. Zero-trust becomes your new best friend since you can't assume anything's safe anymore. Every user, every device gets checked before they touch company stuff. You'll want solid endpoint protection, decent VPNs, and stricter device policies. It's way more work but that's the trade-off for flexibility.
Dude, IoT stuff is a security nightmare. Smart thermostats, cameras, even your printer - they all have garbage default passwords and basically never get updates. I mean, my router's been blinking at me for firmware updates for like 6 months now. These devices are invisible to most security tools too, which sucks. Best thing you can do is make a list of everything connected, throw them on a separate network if possible, and watch what they're actually talking to online. Otherwise you're giving hackers a bunch of easy backdoors into your network.
Dude, you HAVE to keep up with software updates. Hackers literally scan for devices running outdated software - it's like their favorite hobby or something. Those updates aren't just fixing random bugs, they're patching actual security holes that criminals use to break in. I get it, updates are super annoying when you're in the middle of something. But honestly? Skipping them is basically leaving your front door unlocked. Try setting up auto-updates if you can. Or at least don't wait more than a couple days to install the critical ones, especially security patches.
-
I discovered this website through a google search, the services matched my needs perfectly and the pricing was very reasonable. I was thrilled with the product and the customer service. I will definitely use their slides again for my presentations and recommend them to other colleagues.
-
Requested a complete pitch deck. Delivered immediately and with high quality well researched content.