
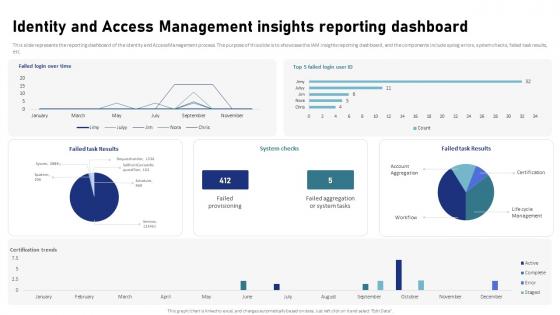
Identity And Access Management Insights Reporting Dashboard IAM Process For Effective Access


Try Before you Buy Download Free Sample Product
 Impress Your
Audience
 100%
Editable
 Save Hours
of Time


 Microsoft PowerPoint
 Microsoft 365
 Claude for PowerPoint
 ChatGPT
 Google Slides
 Microsoft Copilot
This slide represents the reporting dashboard of the Identity and Access Management process. The purpose of this slide is to showcase the IAM insights reporting dashboard, and the components include syslog errors, system checks, failed task results, etc.
People who downloaded this PowerPoint presentation also viewed the following :
Identity And Access Management Insights Reporting Dashboard IAM Process For Effective Access with all 10 slides:
Use our Identity And Access Management Insights Reporting Dashboard IAM Process For Effective Access to effectively help you save your valuable time. They are readymade to fit into any presentation structure.




FAQs for Identity And Access Management Insights Reporting Dashboard IAM Process
So you're looking at a few key pieces here. Authentication proves who you are, authorization controls what you can access. User provisioning handles creating and managing accounts. SSO is huge - saves everyone's sanity honestly. Role-based access controls are where it's at for managing permissions without going crazy. Directory services store all the user data, audit logs track who's doing what (super important for compliance stuff), and you need decent password management tools. The tricky part? Getting everything to play nice together. Otherwise people can't access what they need or you've got security holes everywhere.
Think of IAM like a bouncer for your company's digital stuff - decides who gets in where. You're cutting down attack risks by limiting access to only people who actually need it. Honestly, the audit logs alone are worth it since you can see exactly who did what. Most places give way too many permissions anyway. If someone's login gets stolen, least privilege means they can't wreck everything since they only have bare minimum access. Oh and it stops sketchy employees too, not just outside hackers. I'd start by checking your current permissions - bet you'll find people with access to random systems they haven't used in years.
Look, passwords are basically trash at this point with how often they get leaked. MFA fixes that by adding extra steps - usually your phone or some hardware thing, sometimes even fingerprints. So even if hackers grab your login info, they're still locked out without that second piece. It's honestly the only reason I sleep well at night knowing my accounts are protected. Start with the important stuff first - email, admin access, anything touching sensitive data. Yeah it's slightly annoying at first, but you'll get used to it fast.
Look, the trick is making security invisible for normal stuff. Set up SSO so people log in once and they're good to go. Then add smart authentication that only gets picky when things seem off - like someone logging in from a weird location or device they've never used. Most security headaches come from making users prove themselves constantly. Map out how people actually use your system and spot where you're being annoying for no good reason. Keep the everyday flows smooth, but lock down hard when something's actually suspicious. It's way better than treating everyone like a potential threat 24/7.
Honestly, the worst part is dealing with people who absolutely hate changing their passwords - like, they'll fight you on everything. Legacy systems are a total pain to integrate too. Getting stakeholders to actually decide who needs access to what? Good luck with that. Your IT folks will be pulling their hair out trying to connect all the pieces while business teams complain about new workflows. Oh, and there's this constant tug-of-war between making things secure vs. keeping people productive. Too strict and nobody can get work done. Map out what you've got first, then get the executives on board early - trust me, you'll need them backing you up.
So RBAC is pretty straightforward - you assign roles like "admin" or "editor" and people get whatever permissions come with that role. Sarah's an editor? She gets editor access, done. ABAC is way more detailed though. It looks at tons of factors - where you are, what time it is, your department, how sensitive the data is. Like Sarah might only edit financial stuff during work hours from the office. Honestly, most companies should just start with RBAC since it's easier to manage. Save ABAC for when you've got crazy compliance rules that need super specific controls.
Ugh, compliance is such a pain but you've gotta deal with it. GDPR's probably your biggest headache - explicit consent, deletion requests, the whole thing. SOX covers financial stuff, HIPAA's for healthcare data, and don't forget PCI-DSS if you're handling payments. Honestly, I swear these rules change every other month. Each one has different requirements for data access and retention. Audit trails are mandatory across the board though. My suggestion? Figure out which regulations actually apply to you first. Then just build your IAM around whatever's strictest - saves you from juggling multiple standards later.
So IAM basically handles all the tedious stuff - when someone starts, it sets up their accounts based on their role. People leave or switch teams? It automatically updates their access. Game changer, honestly, because we've all heard those nightmare stories about former employees still logged into everything months later. You can create role-based controls that actually make sense for different jobs, plus set up approval flows for the really sensitive stuff. The audit trails are clutch for compliance too. I'd start by just writing down what you're doing manually now - you'll probably find like 10 things IAM could automate.
Honestly, just pick one identity provider and funnel everything through it. Set up SSO with multi-factor auth - trust me, your users will thank you later instead of constantly resetting passwords. Go with something cloud-native like AWS IAM or Azure AD rather than trying to frankenstein old systems together (been there, it's a nightmare). Role-based access is your friend here, but keep permissions tight. Only give people what they actually need. For anything super sensitive, set up just-in-time access so it's not sitting there permanently. Start by documenting what you've got now - probably more of a mess than you think - then start consolidating. You'll be shocked how much cleaner everything feels once it's centralized.
IAM creates audit trails for everything - tracks who accessed what and when. Super helpful for SOX, HIPAA, GDPR compliance since it automates most of the reporting. Policy enforcement stays consistent across your whole setup too. The risk detection is probably my favorite part though - catches weird access patterns and privilege creep before things get messy. Seriously saves you during audits when you've got all that documentation ready. I'd start by checking your current access against compliance requirements. You'll likely find some gaps that need fixing ASAP.
Honestly, AI and ML are changing everything in IAM right now. Behavioral analytics can spot weird login patterns automatically - way better than the old rule-based stuff. Zero trust is everywhere too, which makes sense since you can't trust anything anymore. Passwordless auth is finally happening (passwords were always garbage anyway). Biometrics and hardware keys are actually becoming normal now. Oh, and there's some interesting blockchain identity stuff emerging, though that's still pretty niche. I'd start playing with behavioral analytics first - it's probably the biggest game-changer you'll see this year.
Start with enabling CloudTrail or whatever your platform uses - seriously, so many companies just ignore this basic stuff. You want comprehensive logging for everything: logins, permission changes, failed attempts, all of it. Focus on privileged accounts especially and watch for weird access patterns. Set up alerts for sketchy behavior like admin logins at 3am or someone suddenly changing a bunch of permissions. The trick is figuring out what normal looks like first, then catching when things get weird. Most platforms have decent built-in audit tools, you just gotta actually configure them properly.
So basically, federated identity lets your team use the same login everywhere - across offices, subsidiaries, even partner companies. No more juggling twenty different passwords (which honestly is such a pain). You set up trust relationships between systems instead of duplicating accounts all over the place. Your London folks can hit the Tokyo database without needing separate credentials there. Really makes life easier for everyone. I'd start by mapping what identity systems you've got now - bet there's more scattered around than you think. The user experience improvement alone makes it worth doing.
Honestly, zero-trust is the way to go for remote work. Multi-factor authentication on literally everything - I know it's annoying but trust me on this one. Single sign-on helps balance that out so your team doesn't hate you. Set up conditional access policies that check location and device health before letting people in. Skip the traditional VPN mess and go with secure web gateways instead. Way cleaner setup. User behavior monitoring catches the weird stuff automatically. Oh, and don't go crazy trying to do everything at once - start with your critical apps first then expand from there.
So for tracking IAM stuff, I'd focus on four main things. Privileged access reviews are huge - like actually checking who has admin rights and fixing it when needed. Time-to-provision matters too because new hires getting stuck without accounts is the worst. Password incidents and failed logins help you catch sketchy activity early. Oh, and compliance findings related to access controls - auditors love that data. Honestly, most companies overthink this, but these basics will show leadership you're improving security without slowing things down. Start here and build from there.
-
Exclusive and extensive collection of templates. Really helped me create a professional presentation in just no time.
-
“One of the best experiences with SlideTeam for my presentation.Everything on time, communication is efficient and price is reasonable. All good in one place.”