



 0 Comment
 Customer Reviews

The audit's scheduled. The auditor's name is on the calendar invite. And somewhere in a shared drive, there's a folder called "ISMS Documentation" that nobody's opened in four months.
That's the real situation most security teams find themselves in. Not that they don't understand information security. They do. But the gap between knowing what an Information Security Management System should look like and actually having one that holds up under scrutiny—that gap is wider than most people admit out loud.
Here's what makes it uncomfortable. An ISMS framework isn't just a policy document. It's a living structure. It covers scope, risk assessment, controls, governance, roles, audit trails—and all of it needs to connect. Pull one thread and the rest starts to unravel. So when someone asks "do we have an ISMS?" the honest answer is usually "we have parts of one."
What makes this worse is the timeline pressure. ISO 27001 certification doesn't wait. Clients ask for it. Contracts require it. Procurement checklists flag it. And the teams responsible are often building the framework while simultaneously running the security operations it's supposed to govern.
That's exactly why these templates exist. Not because the concepts are unclear—most security professionals understand the PDCA cycle, know what Annex A controls look like, can recite the clauses. The problem is translating all of that into a coherent, presentable, defensible set of slides and documents that actually communicate the framework to leadership, auditors, and department heads.
SlideTeam's pre-designed ISMS framework templates handle that translation. They're content-ready structures built around how this information actually needs to be presented—not just stored. Whether it's a gap analysis walkthrough, a governance overview, or a full ISO 27001 compliance deck, the scaffolding is already there.
Here's what's available.
Template 1: Information Security and ISMS Framework into Corporate Control Processes PPT
Integrating an Information Security Management System into corporate control processes is rarely a one-slide conversation. This PowerPoint slide is built for security leads and compliance officers mapping ISMS controls directly to existing governance structures. It makes the connection between ISO 27001 Framework requirements and day-to-day corporate processes clear for leadership. Use it when a boardroom audience needs to see the framework, not just hear about it. The template is 100% editable and customizable.

Download this PowerPoint Template
Template 2: ISMS Framework Template
Clarity commands attention—and this deck delivers it from the first slide. The clean, balanced design merges structured Information Security Management System thinking with visual precision that keeps stakeholders engaged. Flexible color themes let you tailor the deck to your brand without rebuilding from scratch. Use these layouts to present ISMS Implementation roadmaps, policy frameworks, or compliance overviews with professional authority. Transform your information security presentations today. Download this dynamic template now and unlock confident, structured communication.
[product_image id=1481154]
Template 3: ISMS Framework Key Components and Implementation Steps PPT Example
Breaking down an ISMS framework into components and steps is where most presentations lose the room. This PPT preset gives practitioners a structured arc—from foundational principles through actionable implementation milestones. It's the deck a CISO or IT security lead reaches for when walking a cross-functional team through ISMS best practices and real-world framework examples. Use it for ISMS Gap Analysis sessions or onboarding new security stakeholders. The template is 100% editable and customizable.
[product_image id=1652246]
Template 4: Implementing an ISO 27001 Building a Robust ISMS Framework PPT Information
Building an ISO 27001-compliant ISMS isn't just a technical project—it's a governance decision. This slide is built for security architects and compliance managers presenting the case for a formal ISMS framework to senior leadership. It ties ISO 27001 Compliance requirements to practical build steps, making the path from intent to certification visible. Useful in boardroom briefings and client pitches where credibility depends on structure. The template is 100% editable and customizable.
[product_image id=1630013]
Template 5: Strategic Framework for Successful ISMS Implementation PPT Graphics
Turning an ISMS implementation plan into a boardroom-ready narrative takes more than a checklist. This PPT template is built for security program managers who need to present a credible, structured path forward. It covers the strategic layer—objectives, milestones, and governance checkpoints—that leadership actually wants to see. Use it in steering committee reviews or when building the case for ISMS Certification investment. The template is 100% editable and customizable.
[product_image id=1465182]
Template 6: ISMS Framework Policies and Controls Overview PPT Structure
Policies without a clear control structure are just documents nobody reads. This deck drives immediate audience engagement by mapping ISMS Controls and policy categories into a visual, scannable overview. Flexible layouts let you align the structure to your organization's specific Security Control Framework without starting from zero. Use this to present Information Security Policy briefings or compliance overviews to department heads. Transform your ISMS policy presentations today. Download this dynamic template now and unlock structured, stakeholder-ready communication.
[product_image id=1652247]
Template 7: ISMS Framework for ISO 27001 Compliance Explained
ISO 27001 Compliance isn't self-explanatory—and most audiences need it broken down visually. This deck translates the dense requirements of the ISO 27001 Framework into a clear, presentation-ready narrative. Seamless brand alignment through customizable color schemes ensures every slide looks deliberate and credible. Use this for auditor briefings, client compliance reviews, or internal security governance presentations. Elevate your ISO 27001 compliance presentations today. Download this dynamic template now and unlock clear, audit-ready communication.
[product_image id=1652245]
Template 8: How to Build an Effective Exploratory Research Framework PPT Example
Before an ISMS framework can be built, the research phase needs its own structured presentation. This deck empowers security teams and analysts to present exploratory findings with visual clarity and professional precision. The creativity-meets-functionality design ensures that even early-stage insights command attention in the room. Use it for preliminary Risk Assessment Framework reviews or pre-scoping workshops with leadership. Transform your research presentation process today. Download this dynamic template now and unlock structured, evidence-driven communication.
[product_image id=1651691]
Template 9: How to Build an Effective ISMS Framework Today PPT Sample
Building an effective ISMS framework starts with knowing what to present and in what order. This deck gives security professionals a ready-made structure for walking stakeholders through every phase—from scope definition to control implementation. Content-ready layouts mean less time formatting and more time on the actual security conversation. Use this for internal ISMS Documentation sessions or leadership kick-off meetings. Transform your ISMS build presentations today. Download this dynamic template now and unlock a clear, actionable framework narrative.
[product_image id=1651692]
Template 10: ISMS Framework Roles and Governance PPT InfoGraphics
Security Governance Framework conversations often stall because roles aren't clearly visualized. This PPT template is built for ISMS program leads who need to present accountability structures, ownership maps, and governance hierarchies to a mixed audience. It makes who does what—and why it matters—immediately clear to both technical and non-technical stakeholders. Use it for ISMS rollout briefings or governance review sessions. The template is 100% editable and customizable.
[product_image id=1652248]
Template 11: Aligning ISMS Framework with Organizational Security Objectives PPT Sample
Aligning an ISMS framework to organizational security objectives sounds straightforward. In practice, it requires a presentation that connects business goals to security controls in a way leadership actually follows. This slide is built for security managers and CISOs making that case to an executive audience. It ties Cybersecurity Governance priorities to ISMS scope and control decisions with visual clarity. The template is 100% editable and customizable.
[product_image id=1718821]
Template 12: How to Meet ISO 27001 Certification Norms for Incorporation of ISMS Framework
ISO 27001 Certification isn't just a milestone—it's a demonstration of governance maturity. This PowerPoint slide is built for compliance officers showing leadership exactly how the ISMS framework integrates into corporate control processes to meet certification requirements. It covers information security risk management, governance structure, and compliance alignment in one coherent view. Use it in pre-certification briefings or audit preparation sessions. The template is 100% editable and customizable.

Download this PowerPoint Template
Template 13: Implementing Inventory Control Systems for Warehouse Efficiency PPT Sample
Operational control systems demand the same visual rigour as any governance framework. This deck empowers operations managers and warehouse leads to present inventory control system designs with clarity and professional structure. Thoughtfully crafted layouts translate complex workflow data into scannable, stakeholder-ready slides with immediate visual impact. Use these slides for efficiency review meetings or system implementation sign-off presentations. Transform your operational presentations today. Download this dynamic template now and unlock structured, decision-ready communication.
[product_image id=1630012]
Template 14: Risk Management ISMS Framework Best Practices PPT Summary
Risk management inside an ISMS framework is only as strong as the practices behind it. This PPT deck is built for risk officers and security leads presenting ISMS Best Practices to leadership or audit committees. It translates Information Security Risk Management principles into a visual, structured narrative that holds up under scrutiny. Use it for risk review boards, ISMS Audit preparation, or compliance program briefings. The template is 100% editable and customizable.
[product_image id=1693741]
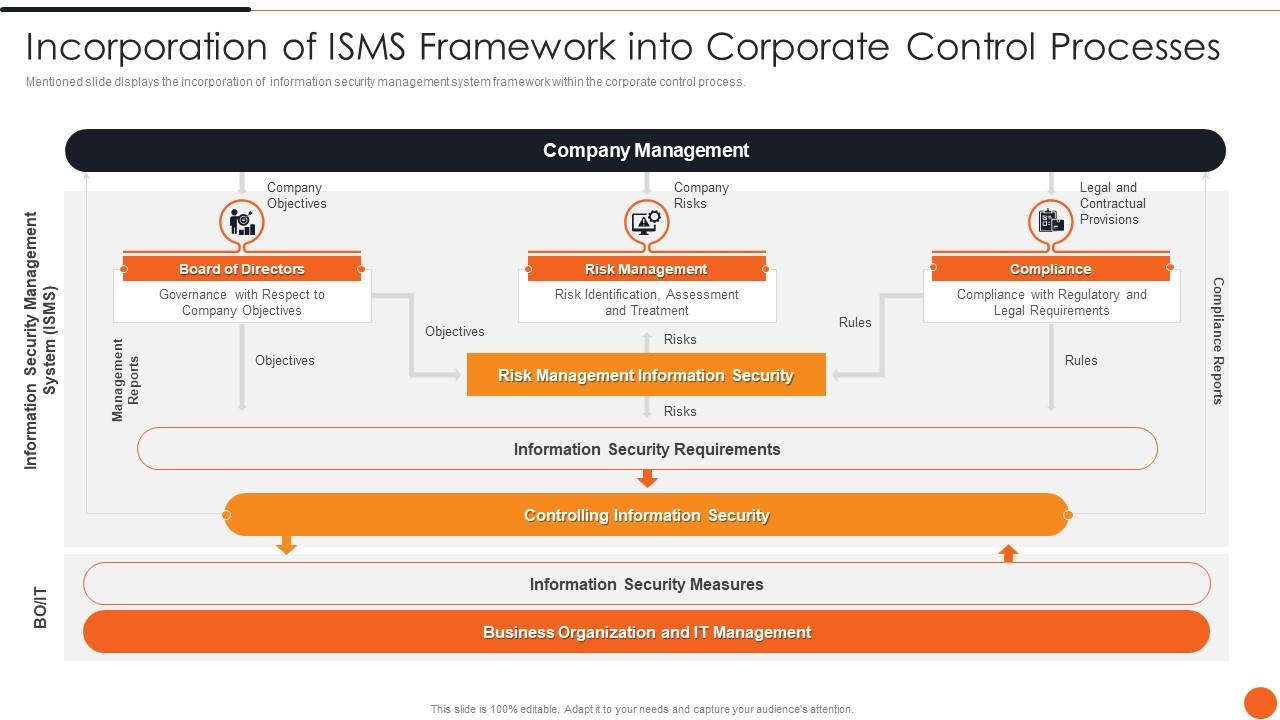
Template 15: Incorporation of ISMS Framework into Corporate Control Processes
The ISO 27001 certification process has specific touchpoints where the ISMS framework must be demonstrably embedded in corporate operations. This slide is built for compliance and governance teams showing auditors exactly how that incorporation works in practice. It covers framework incorporation, scope, and corporate process alignment in a clear, navigable format. Use it in ISO 27001 Audit Checklist reviews or certification walkthrough presentations. The template is 100% editable and customizable.
Download this PowerPoint Template
Deliver Audit-Ready ISMS Framework Presentations with SlideTeam
SlideTeam's PowerPoint templates are the best in the industry for ISMS framework communication—from ISO 27001 Compliance walkthroughs to full Security Governance Framework briefings. These content-ready slides save hours of formatting work and give your presentations the professional structure auditors and leadership expect. Incorporate these ready-made decks into your next ISMS Implementation review or certification preparation session. Deploy these PowerPoint slides to present with clarity, credibility, and confidence.
FAQs on Isms Framework
What is the ISMS framework and how does it differ from other information security management approaches?
An ISMS framework is a structured set of policies, processes, and controls for managing information security risks. Unlike ad hoc security measures, it follows a defined lifecycle—plan, implement, monitor, improve. The key difference from other approaches is its systematic, organization-wide scope. ISO 27001 is the most recognized standard that formalizes this framework with auditable, certifiable requirements.
How does ISO/IEC 27001 serve as the backbone of a robust ISMS framework implementation?
ISO/IEC 27001 provides the clause structure and Annex A control set that an ISMS is built on. It defines what must be documented, monitored, and audited—giving organizations a certifiable baseline. Without it, an ISMS lacks external validation. Most enterprises use ISO 27001 as the primary reference point for scoping controls, managing risks, and demonstrating compliance to clients and regulators.
What are the core components that must be included in an effective ISMS framework structure?
An effective ISMS framework needs four core components: a defined scope, a risk assessment process, a set of security controls mapped to identified risks, and an ongoing monitoring and review cycle. Supporting these are an Information Security Policy, clear ownership of roles, and documented procedures. Without all four working together, the framework won't hold up under audit.
How can organizations determine the appropriate scope of their ISMS framework during initial planning?
Scope definition starts with identifying which assets, processes, locations, and business units are included. Organizations should map data flows first—where sensitive information is created, stored, and transmitted. Then apply boundaries based on regulatory obligations and business risk. A narrow, well-defined scope is easier to certify and maintain than a broad, loosely defined one.
What role does risk assessment play in shaping the policies within an ISMS framework?
Risk assessment tells you which threats and vulnerabilities matter most to your specific assets. Policies are then written to address those identified risks directly—not generically. Without a completed risk assessment, policies tend to be boilerplate and miss real organizational exposures. The risk register should drive every major policy decision inside the ISMS framework.
How does leadership commitment influence the success of an ISMS framework rollout across departments?
Without visible leadership commitment, ISMS implementation stalls at the departmental level. Leaders must approve the Information Security Policy, allocate resources, and hold department heads accountable for compliance. When security is seen as a senior priority, adoption across teams follows. Conversely, when leadership is passive, employees treat ISMS requirements as optional paperwork.
What are the most common gaps organizations overlook when implementing an ISMS framework for the first time?
The three most common gaps are: an undefined or over-broad scope, incomplete risk assessment documentation, and missing evidence of management review. Organizations often build controls but forget to record that those controls were tested and reviewed. Auditors look for evidence, not intentions. A second frequent miss is supplier and third-party risk—often excluded from scope by mistake.
How should an organization prioritize controls within the ISMS framework based on asset criticality?
Start by classifying assets by criticality—high, medium, low—based on business impact if compromised. Apply the strongest controls to high-criticality assets first. Use the risk register to map control gaps to asset value. ISO 27001 Annex A provides the control catalogue; prioritize based on your risk treatment decisions, not on which controls are easiest to implement.