


Attaques de Hameçonnage dans la Formation sur les Cyberattaques PPT




Try Before you Buy Download Free Sample Product
 Impress Your
Audience
 100%
Editable
 Save Hours
of Time


Ce jeu de diapositives PPT couvre en détail les types d'attaques de phishing qui sont le phishing ciblé, le phishing des cadres, le vishing, le smishing, le phishing par e-mail et le phishing par moteur de recherche.
People who downloaded this PowerPoint presentation also viewed the following :
Contenu de cette présentation Powerpoint
Diapositive 2
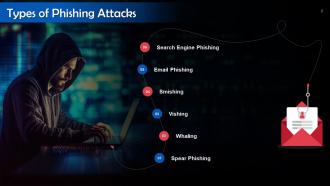
Cette diapositive énumère les types d'attaques par hameçonnage. Ce sont le harponnage, le phishing des grands patrons, le vishing, le smishing, le hameçonnage par courrier électronique et le hameçonnage par moteur de recherche.
Diapositive 3
Cette diapositive parle du harponnage. Le harponnage vise à obtenir un accès illégal à des données confidentielles en ciblant des organisations ou des individus spécifiques.
Diapositive 4
Cette diapositive donne des informations sur le phishing des grands patrons. Une attaque par hameçonnage des grands patrons cible les PDG ou les directeurs financiers pour voler des informations sensibles d'une entreprise. De nombreuses tentatives de phishing des grands patrons visent à tromper la victime pour qu'elle approuve des virements bancaires de grande valeur vers le pirate.
Diapositive 5
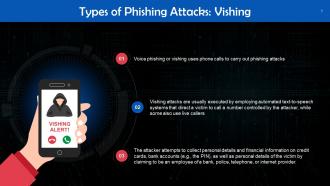
Cette diapositive parle du vishing. Le vishing ou hameçonnage vocal utilise des appels téléphoniques pour mener des attaques par hameçonnage. Les attaques par vishing sont généralement menées à l'aide de systèmes automatisés de synthèse vocale qui dirigent la victime vers un numéro contrôlé par le pirate, tandis que d'autres utilisent des appelants en direct.
Diapositive 6
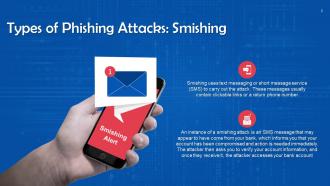
Cette diapositive parle du smishing. Le smishing utilise les messages texte ou le service de messages courts (SMS) pour mener l'attaque. Ces messages contiennent généralement des liens cliquables ou un numéro de téléphone de retour.
Diapositive 7
Cette diapositive met en garde contre le hameçonnage par courrier électronique. Le hameçonnage par courrier électronique est la forme la plus répandue de hameçonnage, où les pirates envoient des courriels à n'importe quelle adresse électronique qu'ils peuvent obtenir.
Diapositive 8
Cette diapositive parle du hameçonnage par moteur de recherche. Dans le hameçonnage par moteur de recherche ou l'empoisonnement des moteurs de recherche, les pirates travaillent pour devenir le premier résultat sur un moteur de recherche en utilisant l'optimisation pour les moteurs de recherche.
Hameçonnage Attaque par déni de service Attaque par force brute Attaque par injection de code Attaque par déni de service distribué Attaque par reniflage de paquets Attaque par usurpation d'identité Attaque par dépassement de tampon Attaque par déni de service par épuisement des ressources Attaque par déni de service par inondation Attaque par déni de service par saturation Attaque par déni de service par épuisement des connexions Attaque par déni de service par épuisement de la bande passante Attaque par déni de service par épuisement de la mémoire Attaque par déni de service par épuisement du processeur Attaque par déni de service par épuisement du disque Attaque par déni de service par épuisement des sockets Attaque par déni de service par épuisement des threads Attaque par déni de service par épuisement des fichiers ouverts Attaque par déni de service par épuisement des descripteurs de fichiers Attaque par déni de service par épuisement des processus Attaque par déni de service par épuisement des ressources système Attaque par déni de service par épuisement des ressources réseau Attaque par déni de service par épuisement des ressources de stockage Attaque par déni de service par épuisement des ressources de calcul Attaque par déni de service par épuisement des ressources de mémoire Attaque par déni de service par épuisement des ressources d'entrée/sortie Attaque par déni de service par épuisement des ressources de sécurité
Utilisez nos types d'attaques de phishing dans la formation sur les cyberattaques PPT pour vous aider efficacement à gagner du temps précieux. Ils sont prêts à s'intégrer dans n'importe quelle structure de présentation.









FAQs for Phishing Attack Types In Cyber
The most common phishing attacks include email phishing, spear phishing, whaling, smishing, vishing, and business email compromise schemes. These attacks increasingly target organizations through sophisticated social engineering, credential harvesting, and domain spoofing techniques, with many financial institutions and healthcare providers finding that comprehensive security awareness training significantly reduces successful breach attempts.
Organizations can effectively train employees through regular simulated phishing exercises, interactive workshops focusing on email verification techniques, awareness campaigns highlighting current threats, and clear reporting protocols for suspicious communications. These comprehensive programs enhance security awareness by teaching staff to identify suspicious links, verify sender authenticity, and recognize social engineering tactics, ultimately reducing successful attacks while building a security-conscious workplace culture.
Social engineering serves as the psychological foundation of phishing attacks, manipulating human emotions like urgency, fear, trust, and curiosity to bypass technical security measures. These techniques exploit cognitive biases and social dynamics, with attackers impersonating trusted entities, creating false emergencies, and leveraging authority relationships, ultimately enabling cybercriminals to extract sensitive information that automated defenses alone cannot protect against.
Spear phishing attacks target specific individuals or organizations with personalized, researched content, while traditional phishing uses generic mass emails sent to thousands of recipients. These targeted attacks leverage detailed reconnaissance about victims' roles, relationships, and interests, enabling cybercriminals to craft convincing messages that significantly increase success rates and bypass standard security awareness training.
Effective phishing mitigation strategies include employee security training, multi-factor authentication, email filtering systems, regular security audits, and incident response protocols. These approaches work by enhancing human awareness, strengthening access controls, and automating threat detection, with many organizations finding that combining technical solutions with ongoing education delivers significantly reduced breach risks and improved security posture.
Whaling is a highly targeted phishing attack that specifically targets high-profile executives, senior management, or other valuable individuals within organizations, rather than casting a wide net like traditional phishing. These sophisticated attacks often involve extensive research and personalized content, with attackers impersonating trusted business contacts, legal entities, or regulatory bodies to deceive executives into revealing sensitive information or authorizing fraudulent transactions.
Anti-phishing tools include email security gateways, machine learning algorithms, URL reputation services, domain authentication protocols, and behavioral analysis systems. These technologies enhance cybersecurity by scanning incoming messages, analyzing sender credibility, and detecting suspicious links, with many organizations finding that integrated solutions significantly reduce phishing threats while streamlining security operations.
Remote work has significantly increased phishing attack prevalence by expanding attack surfaces through personal devices, home networks, and reduced IT oversight, while cybercriminals exploit pandemic-related anxieties and communication gaps. Organizations across sectors like healthcare, finance, and education report 300-600% increases in phishing attempts, as attackers leverage urgent COVID-related themes, fake collaboration platform invitations, and compromised personal email accounts to bypass traditional security perimeters.
Successful phishing attacks can result in data breaches, financial losses, operational disruptions, regulatory penalties, and significant reputational damage for organizations. These incidents often expose sensitive customer information, compromise internal systems, and erode stakeholder trust, with many financial institutions and healthcare organizations finding that recovery costs and compliance violations ultimately impact long-term competitive positioning and market credibility.
Phishers exploit psychological triggers like urgency, authority, fear, and trust to manipulate victims into hasty decisions, often using fake deadlines, official-looking communications, and emotional pressure tactics. These manipulation techniques enhance attack success rates by bypassing rational decision-making, with many organizations finding that employee awareness training significantly reduces susceptibility to such psychological exploitation.
Organizations facing phishing attacks encounter compliance violations, regulatory fines, litigation risks, and potential criminal liability depending on compromised data types. These legal challenges include GDPR penalties, HIPAA violations, and SEC reporting requirements, with many financial institutions and healthcare providers finding that proactive cybersecurity investments significantly reduce liability exposure while demonstrating due diligence.
Notable phishing case studies include the 2016 Democratic National Committee breach through spear-phishing emails, Target's 2013 credential theft affecting 70 million customers, and Anthem's 2015 healthcare data compromise impacting 78.8 million records. These incidents demonstrate how phishing attacks can devastate organizations through massive financial losses, regulatory penalties, and long-term reputation damage, ultimately costing companies millions in recovery efforts.
Individuals can protect personal information by verifying sender authenticity, avoiding suspicious links, using multi-factor authentication, keeping software updated, and regularly monitoring accounts for unusual activity. These protective measures work by creating multiple security layers, enabling early threat detection, and minimizing attack surfaces, with many organizations finding that employee education combined with technological safeguards significantly reduces successful phishing incidents.
Domain spoofing enables cybercriminals to create fraudulent websites that closely mimic legitimate organizations, tricking users into sharing sensitive credentials and financial information. This technique significantly amplifies phishing success rates by exploiting user trust, with financial institutions, e-commerce platforms, and government agencies finding that spoofed domains bypass traditional security awareness, ultimately requiring enhanced verification protocols and employee training.
Multi-factor authentication significantly reduces phishing risk by requiring additional verification beyond stolen passwords, including biometric scans, SMS codes, or hardware tokens. Even when cybercriminals successfully capture login credentials through phishing emails, they cannot access accounts without the second authentication factor, with many financial institutions and healthcare organizations finding that MFA blocks over 99% of automated attacks.
-
Loved the collection. Editing the presentation was seamless with their templates.
-
The presentations are very helpful. I am always able to get appropriate templates for the different topics related to my profession.