
API Testing Powerpoint Ppt Template Bundles


Try Before you Buy Download Free Sample Product
 Impress Your
Audience
 100%
Editable
 Save Hours
of Time


Our API Testing Powerpoint Ppt Template Bundles are topically designed to provide an attractive backdrop to any subject. Use them to look like a presentation pro.
People who downloaded this PowerPoint presentation also viewed the following :
API Testing Powerpoint Ppt Template Bundles with all 22 slides:
Use our API Testing Powerpoint Ppt Template Bundles to effectively help you save your valuable time. They are readymade to fit into any presentation structure.











FAQs for API Testing Powerpoint
So manual API testing is basically you building requests yourself in Postman or whatever - super useful for exploring weird edge cases or when something's acting funky. Automated testing just runs your test scripts over and over without you doing anything. I honestly love the manual stuff for digging into problems at first. But once you've figured things out, automate all that repetitive crap or you'll go crazy. The automated stuff is perfect for regression testing and CI/CD. You really need both though - can't just pick one and call it a day.
Map out all your endpoints first - that's honestly the hardest part. Then hit the happy paths, edge cases, and all those error scenarios that'll bite you later. Status codes matter but don't stop there. Check response schemas, auth flows, rate limits too. Empty requests and huge payloads will break things in weird ways, so test those boundary conditions. Oh and grab a coverage tool so you're not guessing what you've actually tested. I always forget about different data types until something blows up in production.
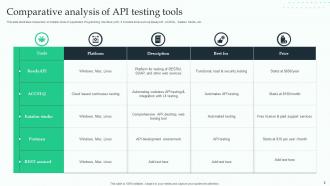
So you've got three main options everyone uses: Postman, REST Assured, and Insomnia. If you're just starting out, go with Postman - the GUI is super friendly and you can literally be testing APIs in like 5 minutes. Already working in Java? REST Assured integrates perfectly with existing test suites. Insomnia's the lightweight option that's way faster than Postman, and honestly the interface is just cleaner. I probably should've mentioned curl but nobody wants to write those commands from scratch anymore lol. Start with Postman though, you won't regret it.
Oh man, good API docs are literally everything when you're testing. Without them you're just guessing at endpoints and parameters like some kind of detective. I've wasted entire afternoons on broken tests because the docs were wrong or missing auth details. Clear documentation helps you write better test cases and actually understand what responses should look like. You'll catch weird edge cases too. But here's the thing - even with perfect docs, you still gotta verify the API actually does what it claims. Sometimes there's random discrepancies that'll mess you up.
Honestly, JMeter or k6 are your best bets for this. Start with maybe 10 concurrent users hitting your endpoints, then ramp it up until stuff starts breaking. I'm partial to Artillery myself - super clean interface. Watch your response times and error rates as you increase load. The 95th percentile metric is way more useful than averages, btw. Don't forget to use realistic payload sizes that match what your actual users send. Postman works too if you're already familiar with it. Just gradually increase until you find where everything falls apart - that's your breaking point.
Dude, mock services are a lifesaver. They let you test API stuff without hitting real external systems that might be broken or cost money every time you ping them. You can fake different responses and error cases that'd be impossible to recreate otherwise. Your tests run way faster too since you control what comes back. Honestly, the best part? You're not being that annoying dev who spam-calls someone's production API while debugging at 2am. Set them up early in your project - I learned this the hard way when trying to test payment failures without actually processing hundreds of fake transactions.
First thing I do is check that whatever I send matches what comes back - sounds obvious but you'd be surprised how often this breaks. Then I throw weird stuff at it like null values and oversized strings because APIs absolutely hate edge cases. Compare your response against the docs to make sure required fields actually show up and data types are right. Here's what I learned the hard way though - always test the full cycle where you modify something then retrieve it back. Start simple with happy path stuff, then get nasty with scenarios that'll expose data corruption. Trust me, it's worth the extra effort upfront.
So first thing - grab OWAWAL's API Security Top 10 list, that's your bible basically. Auth bypass is huge, test if people can skip login entirely. Injection attacks are classic but still everywhere - SQL, NoSQL, command stuff. Check if users can see data they shouldn't (broken authorization). Mass assignment bugs are weirdly common - attackers just modify fields they're not supposed to touch. Rate limiting problems, CORS issues, sensitive data leaking in responses. Oh and insecure deserialization - honestly that one flies under the radar but it'll wreck you. Start with that OWASP list though, covers most of what you need.
So with API versioning, you're basically juggling multiple versions at once - your live one plus whatever new stuff you're pushing out. Each version needs its own test suite since endpoints and responses change between them. Honestly, it's kind of a pain to set up initially but saves you so much grief later. You'll want to test backward compatibility if you're still supporting older versions. Also check that your version headers or URL paths are actually routing things right - I've seen that break more often than you'd think. Start by writing down which versions you support and what's different between them.
REST APIs? Test your HTTP methods hard - GET, POST, PUT, DELETE - plus status codes. That's like 80% of your work right there. Contract testing with Pact is solid if you're doing microservices. SOAP is different though, more about XML schema validation and WSDL stuff. Honestly kind of a pain but at least it's predictable. Don't forget the basics either - boundary testing, error handling, performance checks. I'd probably start with automated tests on your main endpoints first. Then add contract testing later if you need it. Way easier to build up than try to do everything at once.
So basically you'll want to add test scripts as pipeline stages that kick off after your build finishes. Jenkins, GitHub Actions, GitLab CI - they all let you set up test steps using stuff like Postman or pytest. Point your tests at the right environment URLs and make sure they actually fail the pipeline when something breaks (trust me, you don't want busted endpoints hitting prod). Run your smoke tests first, then the deeper integration stuff. Honestly, I'd start with just your most critical APIs and build from there - trying to test everything at once is a headache.
Test your API errors like crazy - both the ones you expect and the weird stuff that'll inevitably break. Validate those HTTP status codes (400s, 500s) and make error messages actually helpful. Most people only test happy paths and that's honestly where everything falls apart. Your API needs to handle malformed requests, missing headers, and garbage data without exploding. Oh and use a consistent error format or your frontend devs will probably murder you. Don't forget timeouts, rate limiting, and auth failures - they happen more than you'd think. Document what "normal" failures look like so nobody panics.
Set up different test accounts with various permission levels - that's your starting point. Store all your API keys and tokens in environment variables or some secure tool, don't hardcode that stuff obviously. Test the happy path first with valid creds, then go after the broken scenarios: expired tokens, wrong permissions, garbage auth headers. OAuth's trickier - either mock the token exchange or use test endpoints if your provider has them (most do these days). Oh, and build some reusable auth helpers early on. Trust me, you don't want to copy-paste credential logic all over your test suite.
So GraphQL testing is weird because there's just one endpoint handling all these complex queries, unlike REST where you hit different URLs. The tricky part? You've got to test field permissions, nested data, and query validation - it gets messy fast. I'd start by mapping your schema's main paths, then test different query combos and mutations. Oh and schema changes are a nightmare if they break existing clients, so definitely check that. GraphiQL beats Postman for this stuff since you can actually explore the schema. Subscriptions add another layer if you're using those too.
Honestly, just get yourself a proper bug tracker like Jira or Linear - makes life so much easier. When you log API bugs, dump everything in there: the endpoint URL, what you sent, what you expected back vs what actually happened, plus those HTTP status codes. Screenshots from your testing tool are nice but the raw data matters more. Oh and definitely test your repro steps first - nothing worse than submitting a ticket only to have dev come back with "can't reproduce this." Trust me on that one. Tag by severity and which API module it affects so your team can prioritize properly.
-
Well-designed and informative templates. Absolutely brilliant!
-
SlideTeam is my one-stop solution for all the presentation needs. Their templates have beautiful designs that are worth every penny!