

Fonctions de hachage dans la formation à la technologie Blockchain Ppt




Try Before you Buy Download Free Sample Product
 Impress Your
Audience
 100%
Editable
 Save Hours
of Time


Ces diapositives couvrent le concept de hachage dans la technologie blockchain. Il comprend la définition, les caractéristiques de la fonction de hachage et le concept d'avalanche. Il couvre également les différents types de fonctions de hachage Secure Hashing Algorithm SHA-2 et SHA-3, RACE Integrity Primitives Evaluation Message Digest RIPEMD, Message Digest Algorithm 5 MD5 et BLAKE2.
People who downloaded this PowerPoint presentation also viewed the following :
Contenu de cette présentation Powerpoint
Diapositive 1
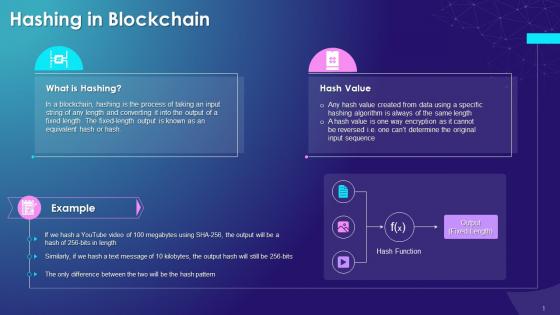
Cette diapositive fournit des informations sur le concept de hachage dans la technologie blockchain. Il comprend également des détails concernant la valeur de hachage et un exemple pour l'illustrer.
Diapositive 2
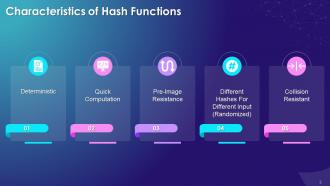
Le but de cette diapositive est de mettre en évidence les multiples propriétés des fonctions de hachage cryptographiques, qui sont déterministes, calcul rapide, résistance à la pré-image, différents hachages pour différentes entrées (randomisées) et résistantes aux collisions.
Notes de l'instructeur :
Les principales caractéristiques des fonctions de hachage cryptographiques sont les suivantes :
- Déterministe : une fonction de hachage donnera toujours la même sortie pour la même entrée. C'est une caractéristique essentielle car si une fonction de hachage donne une valeur différente à chaque fois pour la même entrée, il sera impossible de garder une trace des entrées
- Calcul rapide : une fonction de hachage doit renvoyer rapidement la valeur de hachage pour l'entrée afin d'assurer la haute efficacité du système de blockchain
- Résistance pré-image : une fonction de hachage est difficile à inverser, de sorte qu'il devient impossible de déterminer l'entrée d'origine à partir d'une valeur de hachage
- Modifications de la valeur de hachage avec un changement d'une minute dans l'entrée : même une entrée d'une minute modifie radicalement la valeur de hachage
- Résistant aux collisions : deux entrées différentes n'auront jamais la même valeur de hachage unique
Diapositive 3
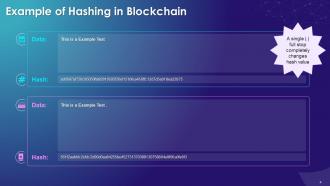
Cette diapositive présente visuellement l'effet d'avalanche du hachage, montrant comment un changement mineur de la valeur d'entrée modifie radicalement la valeur de sortie.
Diapositive 4
La diapositive comprend un exemple pour mettre en évidence le concept d'avalanche dans la blockchain.
Diapositive 5
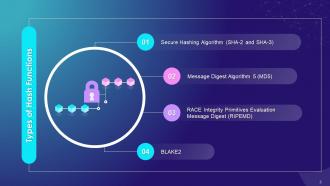
Cette diapositive met en évidence les principales classes de fonctions de hachage cryptographiques telles que l'algorithme de hachage sécurisé (SHA-2 et SHA-3), le résumé de message d'évaluation des primitives d'intégrité RACE (RIPEMD), l'algorithme de résumé de message 5 (MD5) et BLAKE2.
Notes de l'instructeur :
- Chaque catégorie de fonction de hachage a plusieurs algorithmes
- Par exemple, les types de fonctions de hachage SHA-2 incluent SHA-224, SHA-256, SHA-384, SHA-512, SHA-512/224 et SHA-512/256
- Bien que toutes ces fonctions de hachage soient similaires, elles diffèrent légèrement dans la façon dont l'algorithme crée une sortie pour l'entrée en termes de longueur fixe.
- SHA-256 est peut-être la plus célèbre de toutes les fonctions de hachage cryptographique car elle est largement utilisée dans la technologie blockchain. De plus, Satoshi Nakamoto l'a utilisé dans le protocole bitcoin original
Diapositive 6
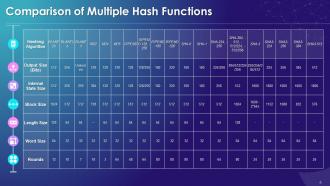
Cette diapositive présente la comparaison de plusieurs fonctions de hachage cryptographiques utilisées dans la blockchain sur plusieurs paramètres tels que la taille de sortie (bits), la taille de l'état interne, la taille du bloc, la taille de la longueur, la taille du mot et les tours.
Hash Functions In Blockchain Technology Training Ppt avec les 22 diapositives :
Utilisez nos fonctions de hachage dans la formation à la technologie Blockchain Ppt pour vous aider efficacement à économiser votre temps précieux. Ils sont prêts à l'emploi pour s'adapter à n'importe quelle structure de présentation.







FAQs for Hash Functions In Blockchain
So basically, a hash function takes whatever data you throw at it and spits out a fixed-size result. The cool part? It's completely one-way. You can generate the hash easily, but good luck trying to reverse-engineer the original data from it. It's like a digital fingerprint that can't be faked or undone. Unlike normal functions where you might solve backwards from the output, hash functions make that practically impossible - which is honestly pretty clever. They're huge in cryptography, password storage, all that security stuff. Whenever you see one, just think "unique signature that can't be reversed."
So basically, the avalanche effect is what makes hash functions actually secure. If you change even one tiny bit in your input, a good hash will flip about half the bits in the output - which is honestly pretty crazy when you think about it. This randomness stops attackers from finding patterns they could exploit. Like, without it, hackers could potentially reverse-engineer data or create collisions way easier. That's why when you're picking hash functions for anything security-related, you'll want to check they have strong avalanche properties first. It's one of those things that separates the decent functions from the garbage ones.
Hash functions are basically everywhere - password storage, databases, blockchain stuff. They create these unique "fingerprints" for any piece of data. Super useful for checking if files got corrupted or tampered with. Hash tables use them too, which is how databases can find your records crazy fast instead of searching through everything. I swear half the internet would break without them. Digital signatures rely on hashing, plus all those verification systems. If you're building anything that needs quick lookups or security checks, definitely worth thinking about where you could throw some hashing in there.
Think of hash functions like really sensitive tamper-proof seals for your data. Change even one tiny bit? You get a totally different hash value. So you can hash something before storing it, then hash it again later - if the values match, nothing's been messed with. Downloads use this all the time (you've probably seen those weird strings of numbers and letters). Password storage, blockchain stuff, digital signatures too. Honestly once you start noticing hash verification, you see it everywhere. It's basically how computers prove "hey, this data is still exactly the same."
So basically cryptographic hashes (like SHA-256) are built for security - they can't be reversed and it's nearly impossible to get two different inputs that produce the same hash. Way slower though. Non-cryptographic ones like CRC32 are lightning fast but totally breakable security-wise, which is fine since they're just for organizing data in hash tables or catching file corruption. Honestly, just think of it this way: need security? Go cryptographic for passwords, blockchain stuff, digital signatures. Just need speed for data processing? Non-cryptographic all the way.
So collision resistance basically means hackers can't easily find two different inputs that spit out the same hash. Pretty crucial stuff. It's like fingerprints - ideally everyone gets a unique one, though crypto gets way messier than that analogy suggests. There's weak collision resistance (can't find a second input matching a specific hash) and strong collision resistance (can't find ANY two matching inputs). Honestly, just stick with SHA-256 and you'll be fine. MD5 is completely broken at this point - I still see people using it and it drives me nuts.
So hash functions are like digital fingerprints for blockchain data - change even one character and the whole thing scrambles. Your crypto transactions get verified through these, and they link all the blocks together so nobody can mess with them. Mining is basically computers racing to solve hash puzzles (honestly pretty wild that people burn electricity for math problems). They also create your wallet address and handle digital signatures. The chain stays secure because tampering with any block would immediately show up when the hash doesn't match. Pretty clever system once you think about it.
So basically, hash functions turn your actual passwords into scrambled nonsense before storing them. Like "password123" becomes "a8f5f167f44f4964e6c998dee827110c" or whatever. If hackers break in, they can't read the real passwords - just gibberish. You can't reverse it either, which is the whole point. When someone logs in, you hash what they typed and check if it matches. Oh and don't use basic SHA stuff - bcrypt or Argon2 are way better since they add salt. Trust me on this one.
Hash functions get called constantly in your app - password checks, database lookups, caching, all that stuff. When they're slow, everything else slows down too. It's honestly pretty annoying when you hit those bottlenecks. But here's the thing - fastest isn't always best. Cryptographic hashing actually wants to be slower (like bcrypt) to stop brute force attacks. For regular data stuff though? Go fast. Really depends what you're building. I'd test with realistic data amounts before deciding. Speed vs security is always a tradeoff you'll have to make.
So basically the crypto world got burned hard by MD5 and SHA-1 breaking, and now everyone's paranoid about it happening again. BLAKE3 and SHA-3 use completely different math under the hood - sponge constructions and way bigger internal states that make them tougher to crack. Quantum computers are the next big worry, so there's a bunch of post-quantum hash functions in development. My take? Definitely ditch SHA-1 if you haven't already, and SHA-3's probably your best bet for anything new you're building.
You'll mostly run into SHA-256, MD5, and bcrypt. For general stuff like data integrity, SHA-256 is rock solid - Bitcoin runs on it, which says something. MD5 is super fast but totally broken security-wise, so only use it for basic checksums. Password hashing? Always go with bcrypt since it's intentionally slow and salts automatically. There's SHA-3 too if you want the shiny new thing, though honestly SHA-256 handles most cases just fine. My rule of thumb: SHA-256 for regular hashing, bcrypt for anything password-related.
So hash functions are like fingerprints for your data - they create these unique signatures that show if anything's been messed with. Digital signatures work by hashing your document first, then encrypting that hash with your private key. Pretty neat trick. When you're authenticating stuff, the system just compares the original hash with a new one from what it received. If they match, you're good to go. The crazy part is how sensitive they are - change even one character and the whole hash goes completely different. Makes tampering basically impossible to hide.
So the tricky part is finding that sweet spot between security and speed. You don't want something so heavy it bogs everything down, but it needs to be strong enough cryptographically. Collision attacks are a nightmare - that's when different inputs give you the same hash. Also can't let people reverse-engineer the original from your output. One thing I learned the hard way - the avalanche effect matters way more than I thought. Even tiny changes should completely scramble your hash. Honestly, just study SHA-256 first before you try building anything yourself. Trust me on that one.
Hash functions need two main things to stay secure: long outputs and good internal randomness. Anything under 256 bits? Way too easy for attackers to break nowadays. The randomness part is kinda weird though - these functions aren't actually random since they're deterministic, but they're designed so tiny input changes create totally unpredictable outputs. That's what makes them work. Honestly, just use SHA-256 or SHA-3 and you'll be fine. MD5 and SHA-1 are basically ancient history at this point - don't even bother with those anymore.
So you'll want to start with distribution analysis - basically checking if your hash function spreads values evenly. Then do collision testing to see how often different inputs give the same hash (fewer = better obviously). Performance benchmarks are key too, especially under different loads. Oh and avalanche testing! People skip this but it's crucial - makes sure tiny input changes create huge output changes. Actually, I'd probably run the distribution test first since it's easiest, then move to collisions if things look decent. The performance stuff can wait until you're happy with the basic functionality.
-
Nice and innovative design.
-
SlideTeam is the way to go when you are in a time crunch. Their templates have saved me many times in the past three months.