
Risk Assessment Of IT Systems Powerpoint Presentation Slides



Try Before you Buy Download Free Sample Product
 Impress Your
Audience
 100%
Editable
 Save Hours
of Time


 Microsoft PowerPoint
 Microsoft 365
 Claude for PowerPoint
 ChatGPT
 Google Slides
 Microsoft Copilot
Risk management identifies, analyzes, and controls threats to an organizations capital and earnings. IT risk management is the application of risk management methods to control IT hazards. Check out our professionally designed Risk Assessment of IT Systems PowerPoint presentation. First, It covers the current IT problems the company faces, including risks reported by the company and their impacts. It also mentions the financial burden to the company. Additionally, the PPT covers the need for IT risk management, IT risk classification, and threat management approach with framework and process. Moreover, it mentions the security criteria and control measures for IT system vulnerabilities, which include the detection and prevention of operational controls and management security controls, along with detailed control measures for technical security risks. Furthermore, the module covers IT security residual risk, IT risk management software, and cost estimation for system audit with a risk mitigation plan with control measures. At last, it highlights the damage control assessment and IT risk management dashboards. Get access to this powerful template now.
People who downloaded this PowerPoint presentation also viewed the following :
Content of this Powerpoint Presentation
Slide 1: This slide introduces Risk Assessment of IT Systems. State your company name and begin.
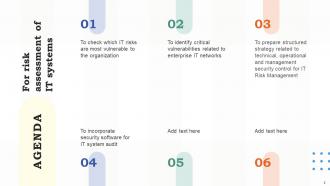
Slide 2: This slide states Agenda of the presentation.
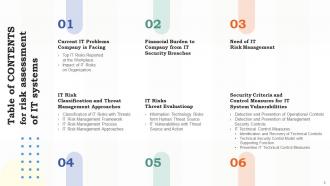
Slide 3: This slide shows Table of Content for the presentation.
Slide 4: This is another slide continuing Table of Content for the presentation.
Slide 5: This slide highlights title for topics that are to be covered next in the template.
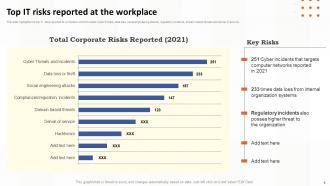
Slide 6: This slide presents Top IT Risks Reported at the Workplace.
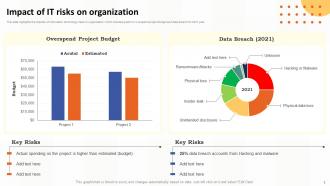
Slide 7: This slide displays Impact of IT Risks on Organization.
Slide 8: This slide highlights title for topics that are to be covered next in the template.
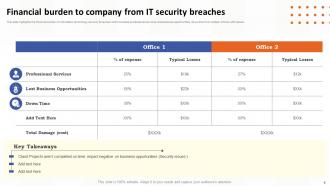
Slide 9: This slide represents Financial Burden to Company from IT Security Breaches.
Slide 10: This slide highlights title for topics that are to be covered next in the template.
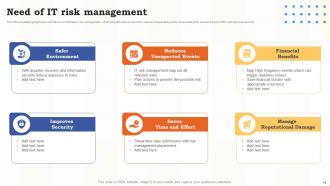
Slide 11: This slide showcases Need of IT Risk Management.
Slide 12: This slide highlights title for topics that are to be covered next in the template.
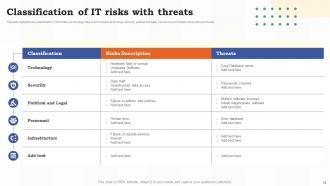
Slide 13: This slide shows Classification of IT Risks with Threats.
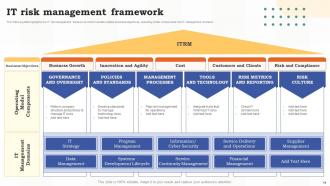
Slide 14: This slide presents IT Risk Management Framework.
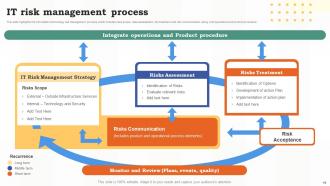
Slide 15: This slide displays IT Risk Management Process.
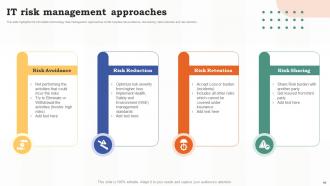
Slide 16: This slide represents IT Risk Management Approaches.
Slide 17: This slide highlights title for topics that are to be covered next in the template.
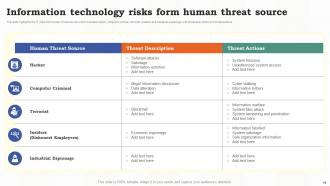
Slide 18: This slide showcases Information Technology Risks form Human Threat Source.
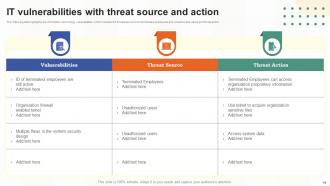
Slide 19: This slide shows IT Vulnerabilities with Threat Source and Action.
Slide 20: This slide highlights title for topics that are to be covered next in the template.
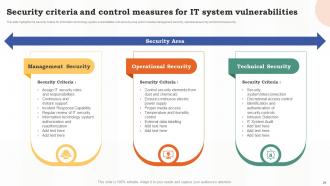
Slide 21: This slide presents Security Criteria and Control Measures for IT System Vulnerabilities.
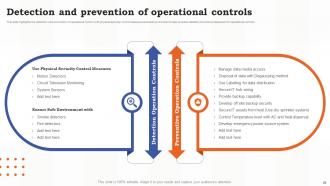
Slide 22: This slide displays Detection and Prevention of Operational Controls.
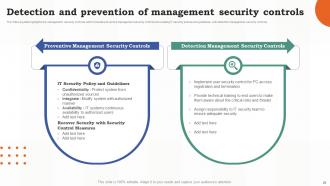
Slide 23: This slide represents Detection and Prevention of Management Security Controls.
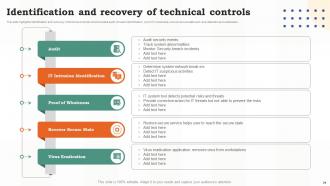
Slide 24: This slide showcases Identification and Recovery of Technical Controls.
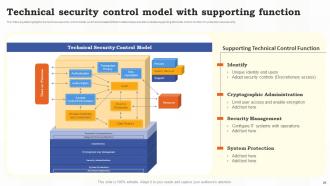
Slide 25: This slide shows Technical Security Control Model with Supporting Function.
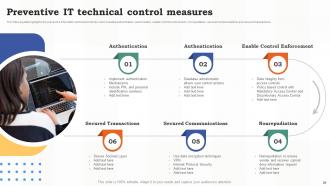
Slide 26: This slide presents Preventive IT Technical Control Measures.
Slide 27: This slide highlights title for topics that are to be covered next in the template.
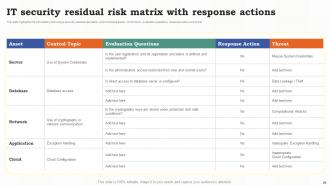
Slide 28: This slide displays IT Security Residual Risk Matrix with Response Actions.
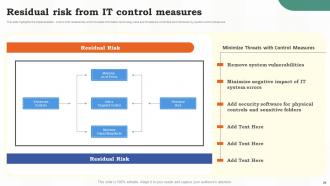
Slide 29: This slide represents Residual Risk from IT Control Measures.
Slide 30: This slide highlights title for topics that are to be covered next in the template.
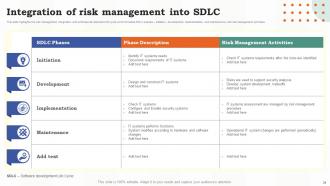
Slide 31: This slide showcases Integration of Risk Management Into SDLC.
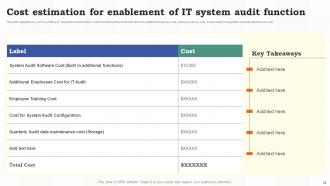
Slide 32: This slide shows Cost Estimation for Enablement of IT System Audit Function.
Slide 33: This slide highlights title for topics that are to be covered next in the template.
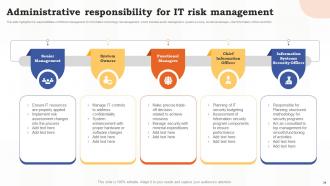
Slide 34: This slide presents Administrative Responsibility for IT Risk Management.
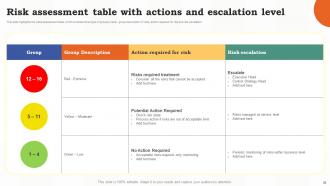
Slide 35: This slide displays Risk Assessment Table with Actions and Escalation Level.
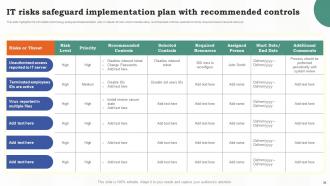
Slide 36: This slide represents IT Risks Safeguard Implementation Plan with Recommended Controls.
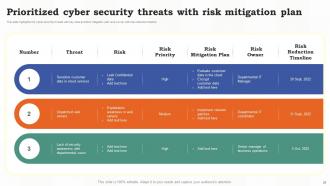
Slide 37: This slide showcases Prioritized Cyber Security Threats with Risk Mitigation Plan.
Slide 38: This slide highlights title for topics that are to be covered next in the template.
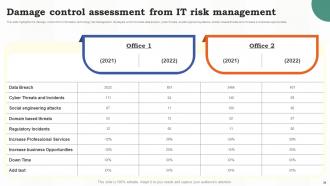
Slide 39: This slide shows Damage Control Assessment from IT Risk Management.
Slide 40: This slide highlights title for topics that are to be covered next in the template.
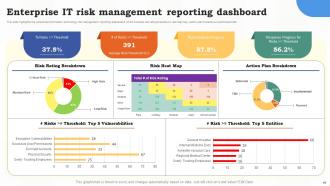
Slide 41: This slide presents Enterprise IT Risk Management Reporting Dashboard.
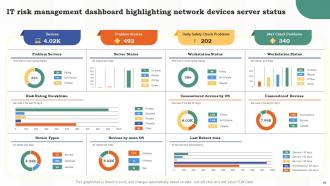
Slide 42: This slide displays IT Risk Management Dashboard highlighting Network Devices Server Status.
Slide 43: This slide contains all the icons used in this presentation.
Slide 44: This slide is titled as Additional Slides for moving forward.
Slide 45: This is Our Goal slide. State your firm's goals here.
Slide 46: This slide provides 30 60 90 Days Plan with text boxes.
Slide 47: This is a Timeline slide. Show data related to time intervals here.
Slide 48: This slide contains Puzzle with related icons and text.
Slide 49: This slide shows Post It Notes. Post your important notes here.
Slide 50: This is a Financial slide. Show your finance related stuff here.
Slide 51: This is a Thank You slide with address, contact numbers and email address.
Risk Assessment Of IT Systems Powerpoint Presentation Slides with all 56 slides:
Use our Risk Assessment Of IT Systems Powerpoint Presentation Slides to effectively help you save your valuable time. They are readymade to fit into any presentation structure.

FAQs for Risk Assessment Of IT Systems
Okay so for risk assessment you need five main things: threat identification, vulnerability analysis, impact assessment, likelihood evaluation, and risk prioritization. First map out what could go wrong, then find your weak spots. Next estimate how bad things might get and how likely each scenario is. Honestly, the prioritization step trips everyone up - there's always too many risks screaming for attention. Don't try to fix everything at once though. Pick your top 3-5 risks and make action plans for those. Oh and set up regular reviews because this stuff changes constantly.
Okay so basically qualitative risk assessment is like saying "this is pretty risky" or "meh, not so bad" - you're using categories instead of actual numbers. Quantitative is when you crunch the data and get real percentages and probabilities. I'd go qualitative first if you're short on time or don't have much data to work with. Heat maps, expert opinions, that kind of thing. Way faster to set up honestly. But for stuff like financial planning or anything where people could get hurt? You really want those hard numbers that quantitative gives you. It just comes down to what info you've got and how exact you need to be.
So you've got a few good routes here. GRC platforms can centralize everything and automate the boring workflow stuff. Monte Carlo simulations are clutch for modeling different scenarios with real probabilities. Heat maps work surprisingly well too - people just get the color-coding thing instantly, which honestly saves so many meetings. Survey tools help you pull input from different teams without chasing everyone down. Oh, and AI analytics can catch patterns you'd probably miss doing it manually. I'd just pick whatever meshes with how you're doing things now and expand from there.
Honestly, just start with a basic risk matrix - plot probability vs impact and you're golden. Score each risk on how likely it is and how much damage it'd cause. Focus on the high-probability, high-impact stuff first (your "red zone" risks). Don't get stuck analyzing every little thing equally - I've seen teams waste weeks doing that. Also check what controls you already have in place. Sometimes a scary-looking risk isn't that urgent if you've got decent safeguards. Pick your top 5 and build action plans from there. Way less overwhelming than trying to tackle everything at once.
Dude, you absolutely need those people in the loop - they see stuff you'll never catch sitting at your desk. Ground-level folks know what actually breaks in their departments, plus they spot weird connections between risks that look totally separate from above. I've watched so many risk assessments completely bomb because some manager thought they had it all figured out solo. Getting them involved early is clutch though - if they help build the solutions, they won't just blow off your recommendations later. Map out who really understands each process first, then just talk to them systematically.
Honestly, once a year is the bare minimum but that's kinda useless advice. Your industry matters way more than some random timeline. High-risk stuff? Do it quarterly. Pretty stable operations can probably get away with annual reviews, but here's the thing - you need trigger events too. Major changes, new regulations, big incidents - that's when risks actually shift. Don't let these turn into paperwork that sits in a drawer somewhere. I'd tie them to real business stuff happening rather than just picking random calendar dates. Way more likely to catch problems that actually matter.
Don't rush through it like some boring checklist - I've watched too many teams just phone it in. You're gonna miss the subtle stuff that actually kills projects if you only focus on obvious risks. Get people from different departments involved because they catch things you'd never think of. Oh, and don't make it too narrow in scope or you'll regret it later. Honestly, the teams that skip regular stakeholder input are setting themselves up for disaster. Set a quarterly reminder to revisit everything since projects change fast and your original assessment becomes useless pretty quick.
You gotta match your risk assessment to whatever industry you're in, honestly. Healthcare? Patient safety and compliance stuff. Manufacturing deals with equipment breaking down and people getting hurt. Tech companies are paranoid about data breaches and their systems crashing - which makes sense. Construction is all about physical dangers and projects running late. Here's what works: look at what's screwed over other companies in your field first. That'll show you the real threats. Then build your whole assessment around those specific risks instead of some generic template.
Track your incident frequency, severity scores, and financial impact first - that's the obvious stuff. But here's the thing, those numbers only show up after something's already gone wrong. You'll want leading indicators too like compliance rates and how fast your team spots new risks. Training completion stats help as well. Set your baseline measurements before you change anything, then watch the trends instead of obsessing over individual data points. Oh and don't skip stakeholder feedback - sometimes the soft stuff tells you more than spreadsheets do.
External stuff can totally flip your risk game upside down. New regulations drop and suddenly what you're doing is sketchy overnight. Market shifts? That "safe" bet becomes a nightmare real quick. 2008 was the perfect example - came out of nowhere and wrecked everyone. You've got to bake these variables into your planning from the start, not scramble later. Stay on top of regulatory changes and market moves so you're not the last one to know. I mean, nobody wants to get caught with their pants down when everything goes sideways.
So scenario analysis basically lets you test your risk models against different "what if" situations that could actually happen. You're not just stuck relying on old data. Think economic crashes, supply chain mess, new regulations - that kind of stuff. Honestly, it's pretty eye-opening once you start doing it. Don't just do best/worst case scenarios though - reality's usually somewhere in the middle, so you need 3-4 realistic ones. Start with your biggest weak spots and build scenarios around those. You'll quickly see where you're most screwed if things go sideways.
Honestly, you can't just do this once and call it done. Build those review cycles right into your process - I'm talking quarterly or every six months where you're actually looking at new threats and how your business has changed. Annual reviews are pretty much useless now since everything moves so damn fast. Different departments will catch stuff you totally missed, so get them involved. Keep an eye out for new regulations and tech shifts too. Oh, and if your business model changes at all, that's gonna create fresh risks you haven't thought about. Think of it more like an ongoing chat than some boring compliance thing you have to check off.
Honestly, the whole field is shifting toward real-time monitoring instead of those pointless annual assessments that nobody reads anyway. AI-powered risk modeling is huge right now. Climate risks are finally getting integrated too - about time. Third-party management is blowing up because supply chains are so messy and connected. Companies are diving deep into behavioral analytics using employee data, which is kinda creepy but makes sense. Oh, and emerging tech risks like deepfakes are becoming a real headache. I'd start by figuring out what you can automate and get real-time data feeds for.
Honestly, you've gotta nail down your risk limits before anything else - like what's actually acceptable vs what'll keep you up at night. Use some kind of scoring system that balances potential upside against how likely things are to go sideways. I've watched way too many teams freeze up trying to avoid every possible risk instead of just managing it smartly. Have real conversations about trade-offs, not just "this feels right" moments. Set up decision rules based on your budget, goals, and whatever regulations you're stuck with. Oh, and definitely create low/medium/high risk categories with different approval chains - saves so much headache later.
Your company culture totally affects how people handle risk assessment - way more than most realize. Risk-averse places get super conservative, imagining worst-case scenarios that'll probably never happen. Meanwhile, bold cultures might brush off real threats or speed through analysis. What matters most? Whether people feel safe reporting bad news without getting thrown under the bus. Culture decides what risks folks will actually talk about and how deep they'll dig. I've seen teams stay quiet about huge red flags just because nobody wanted to be "that person." Create space where people can be honest about what scares them.
-
Great quality slides in rapid time.
-
Been using SlideTeam for some time now…can’t imagine why I wasted all that time in front of the screen trying to make the perfect presentation.