

Introducción a la gestión de riesgos Presentación de diapositivas en PowerPoint





Try Before you Buy Download Free Sample Product
 Impress Your
Audience
 100%
Editable
 Save Hours
of Time


Demuestre que es un auténtico campeón con nuestras diapositivas de presentación en Powerpoint de Introducción a la gestión de riesgos. Definitivamente ganará las guirnaldas.
People who downloaded this PowerPoint presentation also viewed the following :
Contenido de esta presentación de Powerpoint
Diapositiva 1 : Esta diapositiva presenta la Introducción a la gestión de riesgos con imágenes. Indique el nombre de su empresa y comience.
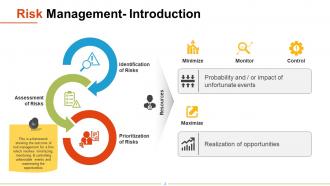
Diapositiva 2 : Esta diapositiva presenta Gestión de Riesgos- Introducción con el siguiente contenido- Minimizar, Monitorear, Controlar, Probabilidad y / o impacto de eventos desafortunados, Realización de oportunidades, Maximizar Recursos, Identificación de Riesgos, Priorización de Riesgos, Evaluación de Riesgos. Este es un marco que muestra el resultado de la gestión de riesgos para una empresa que implica minimizar, monitorear y controlar eventos desfavorables y maximizar las oportunidades.
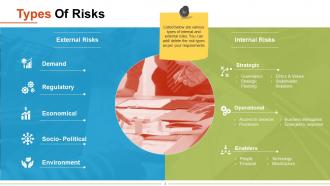
Diapositiva 3 : Esta diapositiva presenta los tipos de riesgos segregados como riesgos externos (demanda, regulatorios, económicos, sociopolíticos, medioambientales). Habilitadores de Riesgos Internos: (Personas, Financiero, Tecnología, Infraestructura). Operacional: (Acceso a Servicios, Procesos, Interrupción de Negocio, Respuesta a Emergencias). Estratégico: (gobernanza, planificación estratégica, ética y valores, relaciones con las partes interesadas)
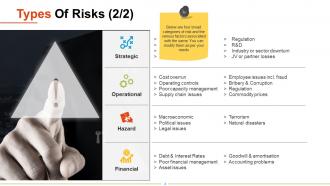
Diapositiva 4 : Esta diapositiva también presenta los Tipos de riesgos detallados para: Estratégicos: Déficit de demanda, Retención de clientes, Problemas de integración, Presión de precios, Regulación, I + D, Industria o caída del sector, JV o pérdidas de socios. Operativo: Exceso de costos, controles operativos, mala gestión de la capacidad, problemas de la cadena de suministro, problemas de los empleados, incl. fraude, soborno y corrupción, regulación, precios de los productos básicos. Peligro: macroeconómico, asuntos políticos, asuntos legales, terrorismo, desastres naturales. Financiero: Deuda y tasas de interés, Mala gestión financiera, Problemas de activos, Fondo de comercio y amortización, Problemas contables. A continuación se presentan cuatro categorías amplias de riesgo y los diversos factores asociados con el mismo. Puede modificarlos según sus necesidades.
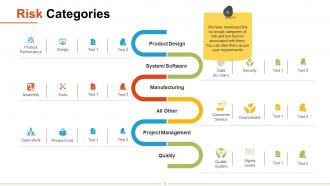
Diapositiva 5 : Esta diapositiva muestra Categorías de riesgo para: Sistema / Software Diseño de producto Calidad de fabricación Gestión de proyectos Todos los demás Hemos mencionado las seis categorías generales de riesgo y algunos factores asociados con ellas. Puede modificarlos según sus requisitos.
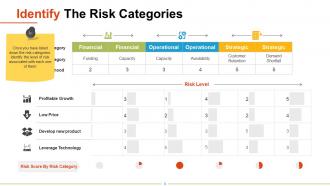
Diapositiva 6 : Esta diapositiva presenta Identifique las categorías de riesgo en forma de tabla: puntuación de riesgo por categoría de riesgo Categoría de riesgo Subcategoría de riesgo en términos de probabilidad y nivel de riesgo una vez que haya enumerado las categorías de riesgo. Identificar el nivel de riesgo asociado a cada uno de ellos.
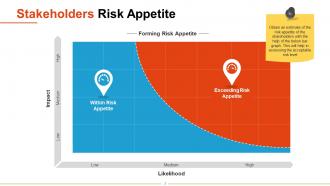
Diapositiva 7 : Esta diapositiva presenta el gráfico de Apetito de Riesgo de las Partes Interesadas en términos de Probabilidad e Impacto. Obtenga una estimación del apetito por el riesgo de los accionistas con la ayuda del gráfico de barras a continuación. Esto ayudará a evaluar el nivel de riesgo aceptable.
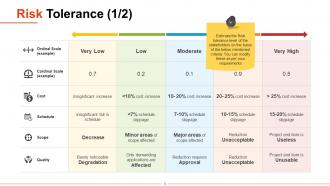
Diapositiva 8 : Esta es la primera diapositiva sobre Tolerancia al riesgo. Estimar el nivel de tolerancia al riesgo de los grupos de interés en base a los criterios que se mencionan a continuación. Puede modificarlos según sus requisitos.
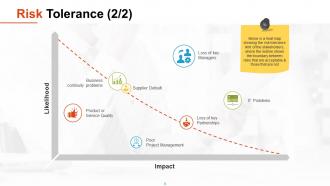
Diapositiva 9 : Esta es la segunda diapositiva sobre Tolerancia al riesgo. A continuación se muestra un mapa de calor que muestra el límite de tolerancia al riesgo de las partes interesadas, donde la línea roja muestra el límite entre los riesgos que son aceptables y los que no lo son.
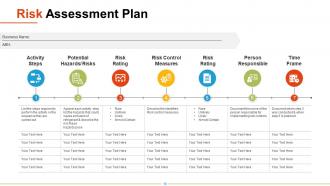
Diapositiva 10 : Esta diapositiva muestra un Plan de evaluación de riesgos con: Nombre de la empresa, ABN, Actividad, Pasos, Peligros / riesgos potenciales, Clasificación de riesgos, Medidas de control de riesgos, Clasificación de riesgos, Persona responsable, Marco de tiempo.
Diapositiva 11 : Esta es la diapositiva del icono Introducción a la gestión de riesgos. Utilice iconos según sus necesidades.
Diapositiva 12 : Esta es una pausa para el café para detener. Puede cambiar el contenido de la diapositiva según sus necesidades.
Diapositiva 13 : esta diapositiva se titula Cuadros y gráficos para avanzar.
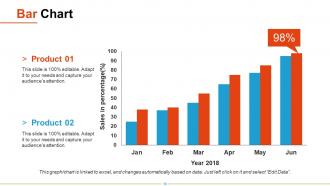
Diapositiva 14 : Esta es una diapositiva de gráfico de barras. Indique especificaciones, comparación de productos / entidades aquí.
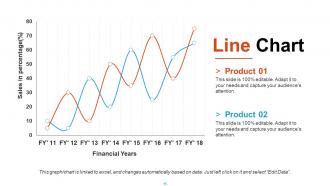
Diapositiva 15 : Esta es una diapositiva de Gráfico de líneas. Indique especificaciones, comparación de productos / entidades aquí.
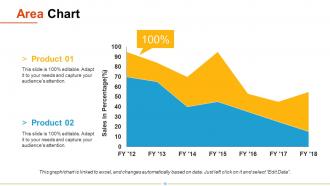
Diapositiva 16 : Esta es una diapositiva de gráfico de áreas. Indique especificaciones, comparación de productos / entidades aquí.
Diapositiva 17 : esta diapositiva se titula Caras adicionales para avanzar. Puede cambiar el contenido de la diapositiva según sus necesidades.
Diapositiva 18 : Esta es la diapositiva Nuestra misión con Misión y metas. Indíquelos aquí.
Diapositiva 19 : Esta diapositiva presenta a Nuestro equipo con el nombre, la designación y el cuadro de imagen.
Diapositiva 20 : Esta es una diapositiva de comparación para mostrar la comparación, información, etc.
Diapositiva 21 : Esta es una diapositiva de puntuación financiera en términos de mínimo, medio y máximo. Indique aquí los aspectos financieros.
Diapositiva 22 : Esta es una diapositiva de la línea de tiempo para mostrar hitos, aspectos destacados del crecimiento, evolución, etc.
Diapositiva 23 : Esta es una diapositiva con imagen de lupa. Especificaciones estatales, información aquí.
Diapositiva 24 : Esta es una diapositiva de imagen de Bombilla / Idea. Indique aquí especificaciones, información, aspectos innovadores.
Diapositiva 25 : Esta es una diapositiva de agradecimiento con dirección, número de calle, ciudad, estado, números de contacto, dirección de correo electrónico.
Introducción a la gestión de riesgos Presentación en PowerPoint Diapositivas con las 25 diapositivas:
Muestre un interés genuino en identificar la causa con nuestras diapositivas de presentación en PowerPoint de Introducción a la gestión de riesgos. Sea capaz de investigar el incidente.
FAQs for Introduction To Risk Management
Okay so you'll need five main pieces: figuring out what risks you're facing, assessing how bad they could be, planning your responses, keeping an eye on things, and having clear ownership. Honestly the first step - just listing everything that could go sideways - is kind of a nightmare but you gotta do it. Score each risk on likelihood and impact, whatever scale makes sense. Then decide if you'll avoid it, reduce it, insure against it, or just live with it. Don't forget regular check-ins so nothing sneaks up on you. Keep it simple at first - you can always get fancier later.
Here's what I'd do - get everyone together for brainstorming sessions. Different departments catch stuff you'll totally miss. Look back at past screw-ups and near-misses, plus check what's happening in your industry. The tedious compliance stuff? Actually super important because that's where problems love to lurk. I'd also chat with stakeholders regularly and do those SWOT things (though honestly, half the time they're just busywork). Set up meetings every few months to talk through this stuff. And write it all down! I swear, the risks you don't document are the ones that'll bite you later.
Honestly, risk assessment is just thinking ahead about what could screw up your project. List out the stuff that might go wrong, then figure out how likely each thing is and how bad it'd be. Do this early when you're planning everything out. I always go with my gut on this - if something's bugging you about the project, write it down. You don't want to be that person crossing their fingers hoping everything works out perfectly. Check back on your list regularly too, because projects change and new problems pop up. It's basically professional worrying, but it actually saves your butt.
So grab a risk matrix and plot everything by impact vs probability. The high-high combos? Those are your fire drills - throw money and attention at them first. Medium stuff needs some basic controls and regular check-ins. But honestly, the low-low risks aren't worth stressing over unless you're swimming in extra budget (which, let's be real, who is?). Focus on what'll actually mess with your operations or cost you serious money. I'd say pick your worst 3-5 risks and hammer those first. Everything else can wait in line.
Cyber attacks are probably the scariest right now - ransomware can literally shut you down overnight. Supply chain issues, regulatory changes, and financial stuff like credit/market swings are huge too. Oh, and don't forget operational risks: losing key people, natural disasters, social media blowups that tank your reputation. What's wild is how everything connects now. One problem triggers three others. My boss learned this the hard way last year. Map out your worst 5-7 scenarios and actually plan responses. Crossing your fingers isn't gonna cut it when things go sideways.
Compliance basically becomes your starting point for risk management, which kinda sucks but whatever. You're stuck building around what regulators want first, then adding your own stuff on top. New data privacy rules drop? Financial reporting changes? You've gotta retrofit everything to meet those standards before you can even think about what actually makes sense for your business. I've seen companies scramble when they're caught off guard by new regulations - it's a nightmare. The trick is trying to stay ahead of regulatory changes so you're not completely screwed when they hit.
Look into GRC platforms - those governance/risk/compliance tools are seriously worth it. ServiceNow and MetricStream are solid options, or something simpler like Riskalyze if you're not dealing with crazy complexity. Data analytics stuff helps you catch problems early, which is huge. Honestly? Even a decent spreadsheet beats winging it, but automated dashboards make life so much easier. Monte Carlo simulations sound fancy but they're actually pretty useful for the heavy-duty analysis. I'd say start small with whatever fits your budget - you can always upgrade once you figure out what you actually need.
Honestly, just track your incident rates - are you dealing with fewer big problems over time? Speed matters too; how fast do you catch new risks and actually do something about it. Near-miss reports are weird because more reports usually means people are more aware (which is good). Cost-wise, compare what incidents cost you versus prevention spending. Your risk assessments should show improvement if things are working. The tricky part is making sure your overall risk is dropping even as you grow the business - that's the real win. I'd pick maybe 2-3 things that actually matter for your situation and stick with tracking those consistently.
Look, first thing you gotta do is figure out who needs what info - your employees aren't gonna need the same updates as customers or whoever regulates your industry. Pick specific people to handle messaging because mixed signals during a crisis? Total nightmare. Draft some templates ahead of time for the usual stuff that goes wrong. Set up how things get escalated and when you'll send updates. Oh, and run practice scenarios - sounds boring but you'll be glad you did. When everything's falling apart, you want simple messages and clear approval processes already in place. Speed matters way more than perfection.
Look, good risk management is basically your crystal ball for making better decisions. You're thinking about expanding into new markets or launching something? Figure out what could blow up first and how likely that actually is. Don't get me wrong - you can't avoid every risk, and honestly you shouldn't try to. But knowing which gambles are worth it? That's gold. The trick is baking this stuff into your planning from day one instead of scrambling when things go sideways. Trust me, it makes your whole strategy so much stronger.
Alright so quantitative risk analysis is all about the hard numbers - percentages, dollar figures, statistical stuff. Gets you super precise results but honestly gathering all that data can be brutal. Qualitative is way more chill - you're just ranking things as high/medium/low risk based on gut feel and experience. Most people I know actually mix both approaches. Start with qualitative to spot your major risks fast, then crunch the numbers on whatever seems scariest. Qualitative's perfect when you're short on time or don't have solid data yet. Just pick whatever fits your situation and timeline.
Yeah, culture totally changes how companies handle risk! Like in Germany and Japan, they're super thorough - endless documentation and detailed frameworks for everything. Other places are way more chill about uncertainty and just wing it (honestly sometimes that works better anyway). Power dynamics matter too. Hierarchical cultures? All risk decisions flow through the top brass. More equal societies let teams make those calls themselves. Oh, and definitely scope out these cultural differences before you try rolling out any risk system across different regions - saves you so many headaches later.
Honestly, AI-powered risk analytics and ESG stuff are taking over everything right now. Climate risk went from zero to "CEO panic mode" in like two years - it's crazy how fast that happened. Cyber resilience frameworks are huge too, especially with all the ransomware attacks lately. Most companies are ditching those old siloed approaches for real-time dashboards that actually predict problems. Supply chain mapping became essential after COVID broke everything. Oh, and definitely audit your current tech first - see what you can automate for risk detection, then start building climate scenarios into your planning. Trust me on that order.
Don't treat crisis management like some separate beast - weave it right into your normal risk stuff. Map out your biggest nightmare scenarios first, then build actual playbooks for each one. Communication chains, who decides what, where resources go. Those tabletop exercises? Actually pretty useful once you get past the corporate buzzword vibe. Your crisis team needs to see the whole picture so they catch domino effects before they spiral. Oh, and whenever you update your risk assessments, revisit those crisis plans too. They should basically talk to each other constantly.
You can't spot every risk on your own - different people notice different problems and have totally different comfort levels with risk. Getting stakeholders involved early gives you way better intel on what might blow up. Trust me, I've seen solid plans get torpedoed because someone important felt left out of the process. They also know stuff about day-to-day operations that you'd never think of. Oh, and the buy-in factor is huge - if they help build the plan, they'll actually follow it. Keep checking with your key people throughout, not just when you're done.
-
amazing
-
Unique research projects to present in meeting.
-
The Designed Graphic are very professional and classic.