
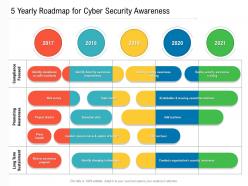
Hoja de ruta de 5 años para la concienciación sobre seguridad cibernética



Try Before you Buy Download Free Sample Product
 Impress Your
Audience
 100%
Editable
 Save Hours
of Time


Visualice su plan de trabajo y comunique sus ideas de manera impactante con nuestra hoja de ruta de 5 años prediseñada para la concienciación sobre seguridad cibernética. Muestre la descripción detallada del proyecto, los entregables clave y los hitos que se deben lograr con la ayuda de nuestro diseño de PowerPoint totalmente personalizable. Puede enfatizar fácilmente los objetivos del proyecto y discutir todas las actividades involucradas de una manera fácil de comprender utilizando nuestro tema PPT diseñado profesionalmente. Este diseño de hoja de ruta de PowerPoint es una herramienta de planificación estratégica perfecta que puede ayudar a mantener el proyecto en marcha. Con nuestro atractivo tema de PowerPoint, puede articular el flujo de trabajo, realizar un seguimiento del progreso del trabajo y tener una visión clara de la meta a alcanzar. Descargue esta hoja de ruta versátil de 5 años para la concienciación sobre seguridad cibernética y ahorre horas de trabajo.
People who downloaded this PowerPoint presentation also viewed the following :
Contenido de esta presentación de Powerpoint
5 Hoja de ruta anual para la concienciación sobre seguridad cibernética con las 2 diapositivas:
Utilice nuestra hoja de ruta de 5 años para la concientización sobre seguridad cibernética para ayudarlo de manera efectiva a ahorrar su valioso tiempo. Están listos para encajar en cualquier estructura de presentación.
FAQs for 5 yearly roadmap for
So for cybersecurity awareness, you want four main things: phishing simulations, training modules on passwords and social engineering, clear incident reporting, and regular updates on new threats. The phishing sims are honestly where you'll see the biggest impact - nothing teaches people like safely screwing up first. Different teams need different focus too. Finance faces way different risks than your IT folks. Oh, and don't do that once-a-year training dump thing. People forget everything immediately. Start with testing where your team's weakest, then build from there.
Track your phishing sim click rates and how often people actually report sketchy stuff - that's where you'll see real change. Password compliance matters too, but honestly the training platform engagement stats are pretty useless. What you really want is quarterly before/after comparisons of actual security incidents. Are people making smarter choices day-to-day? That's the only thing that counts. If you haven't started collecting baseline data yet, do that now or you'll be flying blind later.
Honestly, those one-size-fits-all security trainings are the worst. Visual people need actual phishing examples they can see, not just someone talking at them for an hour. Hands-on learners? Give them simulated attacks or labs where they're configuring stuff. Others learn better through stories about real breaches - that stuff actually sticks. You gotta mix it up though. Videos, workshops, maybe some gamification if you're feeling fancy. Interactive exercises work way better than boring slides. The whole point is hitting different learning styles so people actually remember this stuff instead of zoning out. Trust me, variety keeps everyone engaged.
Honestly, gamification just works because people love competing - even over weird stuff like cybersecurity training. Instead of boring videos, try setting up phishing test leaderboards or badge systems. Teams actually get pumped about "winning" against fake attacks, which is kinda hilarious but effective. The trick is showing progress right away, not waiting months for feedback. You could start super simple - just post monthly phishing scores somewhere visible. I've watched entire departments suddenly care about security training once there's a scoreboard involved. Way better than the usual compliance nonsense everyone ignores.
Start by subscribing to threat intel feeds - honestly, scrolling through cybersecurity news has become part of my coffee routine now. Build in quarterly reviews to see what's actually working. Your IT security team is gold here since they know what's hitting your org. Don't wait for annual training updates though - that's way too slow. Set up quick micro-learning modules you can push out when new threats pop up. The key is making flexibility part of your program from day one, not an afterthought when everything's already built.
You gotta do both at once - they're basically joined at the hip. Give people the actual technical skills first through quick, practical sessions tied to stuff they deal with every day. But here's the thing: without changing behavior, they'll just revert back to "password123" because it's convenient. Follow up with phishing simulations or security challenges to keep those skills sharp. Oh, and definitely celebrate when people get it right - positive reinforcement works so much better than scaring them into compliance. Nobody learns well when they're stressed about messing up.
Definitely hit phishing first - still the biggest threat and those fake emails are getting scary good. Weak passwords are huge too, plus malware downloads when people click stuff they shouldn't. Social engineering is basically just hackers being manipulative, but it works way too often. Oh, and ransomware's a nightmare obviously. USB attacks happen more than you'd think, especially if your team's the type to plug in random drives. Public Wi-Fi risks are real since everyone works from Starbucks now. Insider threats are tricky to bring up without sounding paranoid, but yeah, cover that too. Just use actual examples they'd recognize instead of boring corporate scenarios.
Honestly, I'd go with monthly or quarterly - just don't make it feel like you're trying to catch people being dumb. When someone clicks your fake phishing email, redirect them straight to a quick training thing that shows what red flags they missed. The whole "gotcha!" approach is such a waste of time and just pisses everyone off. Track who's clicking what and use that info to build better training. Like if your accounting people keep falling for fake invoices, create something specific for them. Always do a team chat afterward about what seemed sketchy - those discussions are honestly more valuable than the simulation itself.
Honestly, make your cybersecurity stuff super scannable first - bullet points, bold headers, short paragraphs. People's attention spans are shot. Start with "why should I care" before getting technical, and give them actual steps they can do right now. Skip the jargon or explain it immediately. Real examples work way better than abstract concepts. Here's the thing though - test it with actual people first because what seems obvious to you might be completely confusing to them. Oh, and always give them clear next steps at the end.
Honestly, you've gotta split this up by department - generic training is basically worthless. HR needs the heavy social engineering stuff since they're swimming in employee data all day. Sales should focus more on secure communication and protecting client info. Finance though? Hit them hard with wire fraud and business email compromise training. Those attacks are getting scary sophisticated. Map out what data each team actually touches, then create realistic scenarios they'd encounter. We do tailored phishing sims for each group - way more effective than the usual "don't click bad links" nonsense everyone ignores anyway.
Honestly, you've got three big things to nail down: privacy, consent, and staying compliant with regulations. Be upfront about data collection during training - nobody likes getting blindsided by phishing tests. Get proper consent for monitoring stuff, and if you're dealing with GDPR or HIPAA, make sure you're covered there too. The ethics part is probably the trickiest though. Don't shame people who fail tests (seriously, that backfires hard), and keep everything accessible for everyone. I'd start by checking your current policies for gaps before launching anything new.
Your executives need to walk the walk, not just talk about security in meetings. Have them take the same training as everyone else - I've seen way too many places where leadership preaches security then immediately asks IT to bypass their own rules because it's inconvenient. Make sure they're actually following policies and sharing when they mess up or learn something new. That builds real trust. Invest in decent training budgets too. Celebrate the wins, don't just panic when something breaks. Leadership has to make it clear this isn't just "an IT problem."
Honestly, the biggest shift I'm seeing is interactive stuff replacing those awful click-through modules we all used to hate. Companies are finally doing microlearning - like short monthly sessions instead of those brutal all-day training marathons. Gamification actually works too, which surprised me. Leaderboards and badges get people competing. What's really smart though is measuring if behavior actually changes, not just who finished the course. Some places are integrating training right into their security tools, so if you click something sketchy, boom - instant lesson. I'd definitely try phishing simulations first if you're looking to pilot something new.
Honestly, remote work throws all your old security training out the window. People are logging in from random coffee shops and sketchy home networks now. You can't just tap someone on the shoulder when something looks fishy anymore, which is actually pretty inconvenient. Focus your training on VPN basics and help them spot those phishing emails that specifically target remote workers - they're getting sneaky about it. Make everything mobile-friendly since half your team's probably checking emails on their phones anyway. Oh, and set up some kind of easy way for people to report weird stuff without jumping through hoops.
Honestly, the biggest thing is making people feel safe to report stuff without getting fired or blamed. Fear kills reporting faster than anything. Set up easy channels - dedicated email, Slack, whatever works for your team. Then actually respond when they use it! I'd throw in some small rewards too, like shoutouts in meetings or maybe gift cards for good catches. Oh, and definitely tell people what happened after they report something. Nobody wants to feel like they're shouting into the void. Once your team sees their reports actually lead to action, they'll keep flagging weird stuff. Trust me on this one.
-
Enough space for editing and adding your own content.
-
Visually stunning presentation, love the content.
-
Unique and attractive product design.