

Network load balancer it powerpoint presentation slides





Try Before you Buy Download Free Sample Product
 Impress Your
Audience
 100%
Editable
 Save Hours
of Time


The Network Load Balancing NLB functionality uses the TCP or IP networking protocol to disperse traffic among several servers. Here is an efficiently designed Network Load Balancer IT template that gives a brief idea about a network load balancer company and the need for network load balancing in businesses. Also, it talks about various business problems and organization faces and how NLB can help solve those problems. In this Network Load Balancer PowerPoint Presentation, we have covered the overview of network load balancer by describing its features, working, components, relationship with software components, and architecture. In addition, this NLB PPT contains use cases of the network load balancer, its hardware and software requirements, NLB security strategies, methods, and tools such as Network Load Balancer Manager. Furthermore, this Elastic Network Load Balancer template contains a step-by-step implementation process, monitoring of NLB, and training program for IT team members. Lastly, it comprises a 30-60-90 days plan, a roadmap, and an NLB performance tracker dashboard. Customize this 100 percent editable and insightful template now.
People who downloaded this PowerPoint presentation also viewed the following :
Content of this Powerpoint Presentation
Slide 1: This slide introduces Network Load Balancer (IT). State Your Company Name and begin.
Slide 2: This is an Agenda slide. State your agendas here.
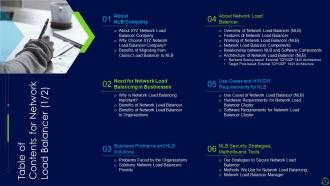
Slide 3: This slide presents Table of Content for the presentation.
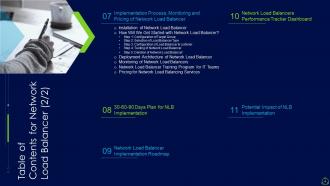
Slide 4: This is another slide continuing Table of Content for the presentation.
Slide 5: This slide shows title for topics that are to be covered next in the template.
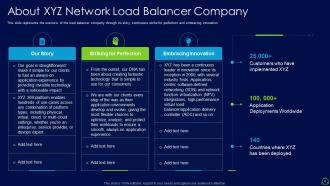
Slide 6: This slide represents the overview of the load balancer company through its story.
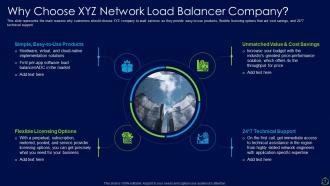
Slide 7: This slide showcases Why Choose XYZ Network Load Balancer Company.
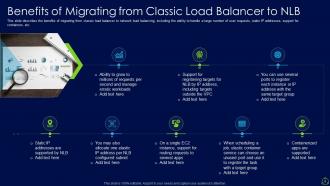
Slide 8: This slide describes the benefits of migrating from classic load balancer to network load balancing.
Slide 9: This slide shows title for topics that are to be covered next in the template.
Slide 10: This slide depicts two main reasons why network load balancing is essential to achieve high availability.
Slide 11: This slide represents the benefits of the network load balancer, including naming abstraction, cost and performance advantages, etc.
Slide 12: This slide showcases Benefits of Network Load Balancer to Organizations.
Slide 13: This slide shows title for topics that are to be covered next in the template.
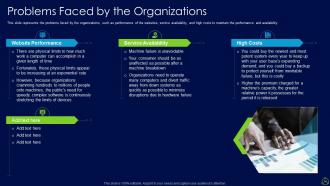
Slide 14: This slide represents the problems faced by the organizations, such as performance of the websites, service availability, etc.
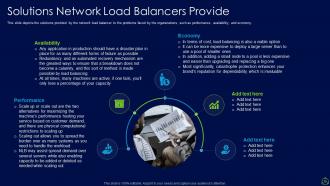
Slide 15: This slide depicts the solutions provided by the network load balancer to the problems faced by the organizations.
Slide 16: This slide shows title for topics that are to be covered next in the template.
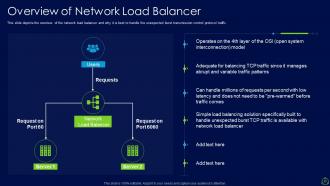
Slide 17: This slide presents overview of the network load balancer and why it is best to handle the unexpected burst transmission.
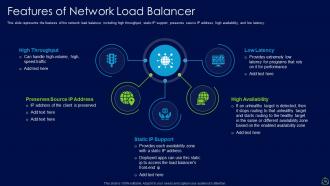
Slide 18: This slide represents the features of the network load balancer, including high throughput, static IP support, preserves source, etc.
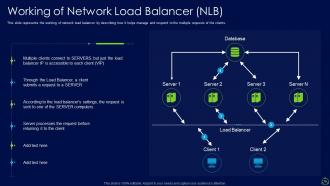
Slide 19: This slide showcases working of network load balancer by describing how it helps manage and respond to the multiple requests.
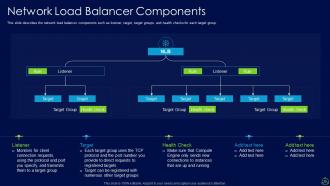
Slide 20: This slide describes the network load balancer components such as listener, target, target groups, etc.
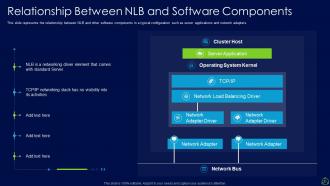
Slide 21: This slide shows Relationship Between NLB and Software Components.
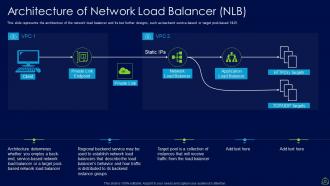
Slide 22: This slide displays the architecture of the network load balancer and its two further designs, etc.
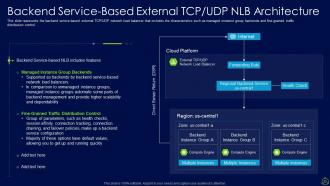
Slide 23: This slide showcases Backend Service-Based External TCP/UDP NLB Architecture.
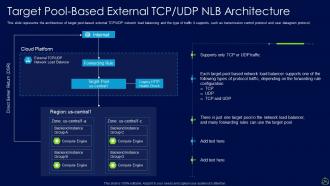
Slide 24: This slide represents the architecture of target pool-based external TCP/UDP network load balancing.
Slide 25: This slide shows title for topics that are to be covered next in the template.
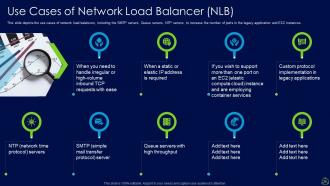
Slide 26: This slide represents the use cases of network load balancers, including the SMTP servers, Queue servers, etc.
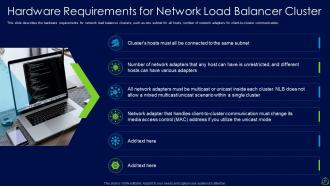
Slide 27: This slide showcases Hardware Requirements for Network Load Balancer Cluster.
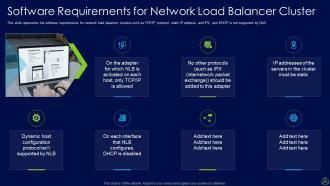
Slide 28: This slide presents Software Requirements for Network Load Balancer Cluster.
Slide 29: This slide shows title for topics that are to be covered next in the template.
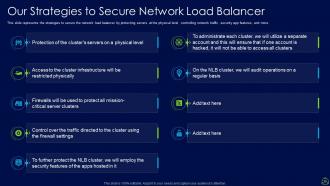
Slide 30: This slide displays Our Strategies to Secure Network Load Balancer.
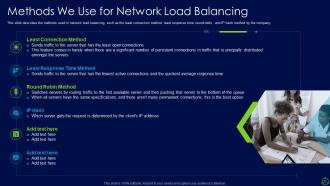
Slide 31: This slide describes the methods used in network load balancing, such as the least connection method, least response time, etc.
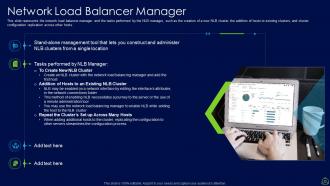
Slide 32: This slide represents the network load balancer-manager and the tasks performed by the NLB manager.
Slide 33: This slide shows title for topics that are to be covered next in the template.
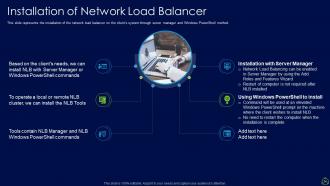
Slide 34: This slide represents the installation of the network load balancer on the client’s system through server manager.
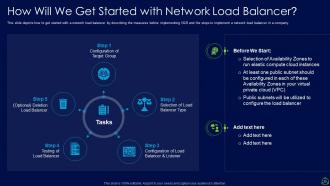
Slide 35: This slide displays How Will We Get Started with Network Load Balancer.
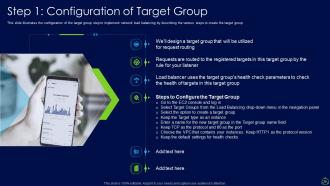
Slide 36: This slide illustrates the configuration of the target group step to implement network load balancing.
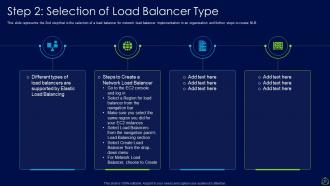
Slide 37: This slide represents the 2nd step that is the selection of a load balancer for network load balancer implementation in an organization.
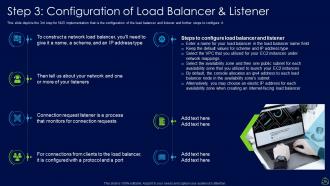
Slide 38: This slide depicts the 3rd step for NLB implementation that is the configuration of the load balancer.
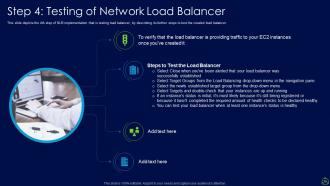
Slide 39: This slide showcases the 4th step of NLB implementation that is testing load balancer, by describing its further steps to test the created load balancer.
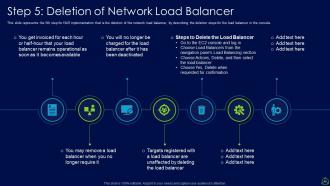
Slide 40: This slide represents the 5th step for NLB implementation that is the deletion of the network load balancer.
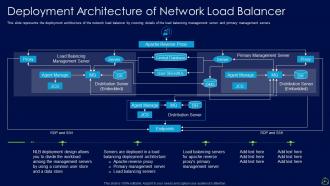
Slide 41: This slide presents the deployment architecture of the network load balancer by covering details of the load balancing management server.
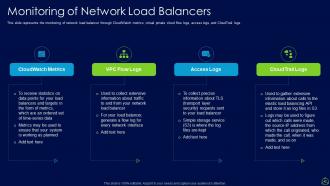
Slide 42: This slide represents the monitoring of network load balancer through CloudWatch metrics, virtual private cloud flow logs, etc.
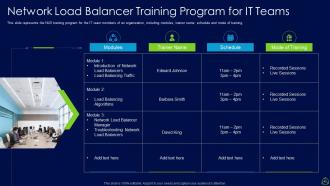
Slide 43: This slide showcases Network Load Balancer Training Program for IT Teams.
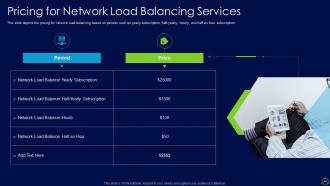
Slide 44: This slide depicts the pricing for network load balancing based on periods such as yearly subscription, half-yearly, hourly, etc.
Slide 45: This slide shows title for topics that are to be covered next in the template.
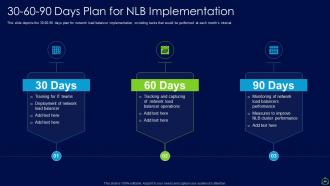
Slide 46: This slide displays 30-60-90 Days Plan for NLB Implementation.
Slide 47: This slide shows title for topics that are to be covered next in the template.
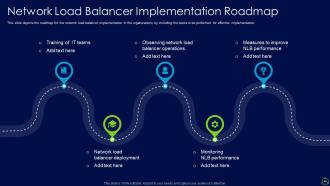
Slide 48: This slide depicts the roadmap for the network load balancer implementation in the organizations.
Slide 49: This slide shows title for topics that are to be covered next in the template.
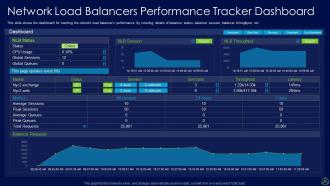
Slide 50: This slide presents Network Load Balancers Performance Tracker Dashboard.
Slide 51: This slide shows title for topics that are to be covered next in the template.
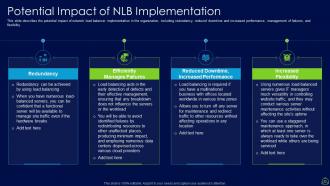
Slide 52: This slide describes the potential impact of network load balancer implementation in the organization.
Slide 53: This slide displays Icons for Network Load Balancer (IT).
Slide 54: This slide is titled as Additional Slides for moving forward.
Slide 55: This is Our Mission slide with related imagery and text.
Slide 56: This slide depicts Venn diagram with text boxes.
Slide 57: This is About Us slide to show company specifications etc.
Slide 58: This slide displays Mind Map with related imagery.
Slide 59: This slide contains Puzzle with related icons and text.
Slide 60: This slide shows Post It Notes. Post your important notes here.
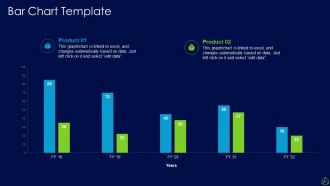
Slide 61: This slide presents Bar chart with two products comparison.
Slide 62: This is Our Goal slide. State your firm's goals here.
Slide 63: This is a Thank You slide with address, contact numbers and email address.
Network load balancer it powerpoint presentation slides with all 68 slides:
Use our Network Load Balancer IT Powerpoint Presentation Slides to effectively help you save your valuable time. They are readymade to fit into any presentation structure.





FAQs for Network load balancer it
So basically a Network Load Balancer spreads incoming traffic across multiple servers so none of them crash from being overloaded. It sits between users and your app servers, routing requests to healthy instances based on stuff like current load. Pretty much like a traffic cop (I know, weird analogy but it works). Health checks happen automatically too - if a server dies, traffic just goes to the others. You'll definitely need one if you're expecting traffic spikes or want high availability. Honestly saved my ass more than once when things got busy.
Oh right, so NLBs work at Layer 4 and ALBs at Layer 7. Basically NLBs just look at IP addresses and ports - they're crazy fast, like millions of requests per second fast. ALBs are way smarter though, they actually dig into your HTTP requests and can route based on URL paths, headers, that kind of stuff. Honestly I'd say NLBs are your speed demons when you need pure performance. ALBs shine when you need fancy routing logic. For simple TCP/UDP stuff, NLB's probably your best bet.
Honestly, you'd want a Network Load Balancer when you're dealing with insane traffic - like millions of requests per second. They work at Layer 4, so they're just looking at IP addresses and ports, not digging into the actual content. Super fast because of that. Perfect for TCP/UDP stuff, gaming servers, or IoT connections where every millisecond matters. Also preserves client IP addresses which can be clutch. I'd skip the ALB if you're not doing HTTP and latency is killing you. They're basically built for serious scale without the processing overhead.
So basically, network load balancers spread your traffic across multiple servers in different zones automatically. When one server dies (and it will happen), traffic just gets routed to the healthy ones - users don't even know anything went wrong. Health checks run constantly to catch issues early. Honestly the cross-zone thing is pretty clutch for avoiding outages. You can swap servers in and out for maintenance without any downtime too, which is nice. I'd set up at least 2-3 instances across different zones - that's where you'll really see the benefits kick in.
Monitor your active connections and new connections per second first - that shows your traffic patterns. Response time matters tons since slow pages kill user experience. Target health checks are honestly the most critical thing though, because unhealthy backends mean dropped requests. Track your throughput (bytes processed) and watch for connection errors too. Oh and definitely set up CloudWatch alarms for all this stuff. Trust me, you want alerts hitting your phone before customers start complaining about outages.
Honestly, I'd go with a Network Load Balancer if you need to scale fast without dealing with physical hardware nonsense. Hardware ones are solid until you max them out - then you're waiting weeks for new equipment while your site crashes. With NLBs you can handle crazy traffic spikes instantly, plus no upfront costs or maintenance headaches. They're perfect for unpredictable traffic or cloud apps. I mean, spinning one up takes literally minutes instead of calling vendors and waiting forever. If you're already on AWS and need to handle millions of requests, NLB is a no-brainer.
So NLBs do SSL termination but at the connection level, not application level like ALBs. Basically it decrypts your SSL/TLS traffic with your cert, then sends plain HTTP to your backend servers. Pretty nice since it takes that heavy encryption work off your servers. The cool part? You still get the original client IPs even after termination - which honestly beats ALBs for logging stuff. Oh and make sure your ACM certificate's set up right and your security groups allow both the encrypted and plain traffic ports. That part always trips people up.
So basically your NLB pings your backend servers constantly to see if they're actually alive and working. If one fails the health check, it just stops routing traffic there automatically - which is honestly pretty cool. You don't want users hitting broken endpoints, right? The trick is setting up a lightweight health check path that actually tests if your app works, not just whether the server boots up. I learned this the hard way when our health checks were too basic. You can tweak the intervals and what counts as "healthy" depending on your setup.
So basically, session persistence keeps users connected to the same backend server throughout their whole session instead of randomly jumping around. You set it up with sticky sessions - the load balancer just remembers which server handled someone's first request and keeps routing them there. Really matters for apps storing session data locally, like shopping carts or login info. Otherwise people lose everything mid-checkout, which honestly drives me crazy when it happens to me. You've got two main options: source IP persistence or application-controlled cookies, depending on what you're building.
So basically, load balancers sit between your users and servers, which hides your actual server IPs from attackers. They spread traffic around so no single server gets hammered during an attack. DDoS protection gets way easier too. Most of them work with services like CloudFlare or AWS Shield - honestly that combo is pretty solid. You can set rules to block sketchy traffic patterns or only allow certain sources. Oh, and you get one central spot to control everything instead of managing security on each server individually. Makes your whole setup way less exposed.
Health checks will drive you absolutely nuts if you're not careful. Too strict and they'll kill perfectly good instances, too loose and you're sending traffic to dead servers. SSL certs are annoying too - especially juggling multiple domains and staying on top of renewals. Oh, and connection draining during deployments trips up tons of people (learned that one the hard way). Definitely test your health check settings in staging first. Also keep a spreadsheet or something for cert expiration dates because getting paged at 2am for expired SSL is the worst.
Honestly, the algorithm makes or breaks your load balancing. Round Robin just goes server 1, 2, 3, repeat - works fine if all your servers are identical twins (spoiler: they're not). Least Connections is way smarter though. It sends new requests to whoever's got the least stuff going on right now. Your request processing times are gonna vary no matter what you do, so this handles real traffic much better. I'd go with Least Connections from the start. Round Robin feels like something from 2005 at this point.
So for NLB scaling, focus on target capacity and connection distribution first. Your backend servers need to actually handle the extra load - can't tell you how many times I've seen people forget that part lol. Cross-zone load balancing is worth considering if you're using multiple AZs, though it'll hit your costs a bit. Watch those target response times like a hawk during scaling. Honestly, start small and scale up gradually instead of going all-in right away. You'll catch bottlenecks way easier that way. Health check intervals matter too but they're not usually the main issue.
So basically you'd set your NLB as the origin for your CDN. Static stuff gets cached at edge locations, dynamic requests go back through the NLB to your servers. It's honestly a pretty solid setup - you get fast static content delivery plus high availability for the dynamic bits. CDN handles the caching while your load balancer keeps distributing traffic properly. Oh, and make sure those health checks are dialed in right or you'll end up routing to dead servers (learned that one the hard way). Works really well once it's running though.
NLBs are actually faster than other load balancers since they work at Layer 4 - just routing by IP and port without digging into packet contents. You're looking at single-digit millisecond latency, which honestly makes a huge difference for anything performance-critical. They can handle millions of requests per second too, so traffic spikes won't crush your users. The downside? You lose Layer 7 features like content-based routing, but that might not matter for your use case. I'd definitely track your response times before and after to see the actual improvement numbers.
-
Great product with highly impressive and engaging designs.
-
Easily Understandable slides.